vault backup: 2026-01-05 13:03:55
This commit is contained in:
 windyboy
+3347
File diff suppressed because it is too large
Load Diff
@@ -0,0 +1,160 @@
|
||||
---
|
||||
page-title: "How to Flush DNS on Mac – MacOS Clear DNS Cache"
|
||||
url: https://www.freecodecamp.org/news/how-to-flush-dns-on-mac-macos-clear-dns-cache/
|
||||
date: "2024-10-28 11:00:36"
|
||||
---
|
||||

|
||||
|
||||
In this tutorial, you will learn why flushing your DNS cache is important, and how you can clear the cache on your local system.
|
||||
|
||||
Here is what we'll discuss in this guide:
|
||||
|
||||
1. [What is DNS cache?](https://www.freecodecamp.org/news/how-to-flush-dns-on-mac-macos-clear-dns-cache/#intro)
|
||||
1. [Why flushing DNS cache is important](https://www.freecodecamp.org/news/how-to-flush-dns-on-mac-macos-clear-dns-cache/#why)
|
||||
2. [How to flush DNS cache on MacOS](https://www.freecodecamp.org/news/how-to-flush-dns-on-mac-macos-clear-dns-cache/#howto)
|
||||
1. [How to access the terminal application on MacOS](https://www.freecodecamp.org/news/how-to-flush-dns-on-mac-macos-clear-dns-cache/#terminal)
|
||||
2. [How to clear DNS Cache for your MacOS version](https://www.freecodecamp.org/news/how-to-flush-dns-on-mac-macos-clear-dns-cache/#version)
|
||||
|
||||
## What is DNS Cache?
|
||||
|
||||
DNS acts much like an internet phonebook. Think of what a phonebook does – it maps a person's name to their respected phone number.
|
||||
|
||||
DNS (short for Domain Name System) maps domain names to their associated IP addresses.
|
||||
|
||||
A domain name, such as `freecodecamp.org`, is easily read, understood, and recalled by humans.
|
||||
|
||||
IP addresses (IP is short for Internet Protocol) is an address that is machine-readable and consists of a unique series of numbers. These numbers identify a device connected to the Internet.
|
||||
|
||||
Their format is not that human-friendly since it is hard to remember an exact sequence of numbers each time you want to visit a website.
|
||||
|
||||
DNS then maps `freecodecamp.org` to its associated IP address - `104.26.3.33`.
|
||||
|
||||
Think of the DNS cache as a local storage area on your Mac.
|
||||
|
||||
It temporarily stores and keeps track of your computer's activity records like recent website visits.
|
||||
|
||||
Each time you visit a website by typing its URL (short for Uniform Resource Locator), the DNS cache will save the IP address associated with that website.
|
||||
|
||||
When you visit that same website for the second time, the lookup process is more efficient, and the lookup time is much shorter.
|
||||
|
||||
It helps save significant time.
|
||||
|
||||
### Why Flushing DNS Cache Is Important
|
||||
|
||||
You should flush the DNS cache for a few reasons.
|
||||
|
||||
The two most important ones are:
|
||||
|
||||
1) **Flushing DNS is a helpful step for troubleshooting Internet connectivity issues**.
|
||||
|
||||
You may be getting DNS errors in your browser, such as the 'DNS Server Not Responding' message when trying to access a site and establish a connection.
|
||||
|
||||
Keep in mind that your local cache information can become outdated over time.
|
||||
|
||||
When DNS updates happen on a website, your Mac is still using the old, inaccurate information to load the requested page.
|
||||
|
||||
Flushing the DNS cache makes sure cache information is up to date.
|
||||
|
||||
2) **Flushing the DNS cache prevents network security threats, malicious attacks, and DNS cache poisoning from happening**.
|
||||
|
||||
Hackers can access and corrupt your saved DNS cache records.
|
||||
|
||||
For example, they could manipulate and change the IP address associated with a Domain Name of a website you have already visited and map it to a malicious one.
|
||||
|
||||
The next time you request to access that same website, there will be a redirection to a fake and corrupted URL.
|
||||
|
||||
Hackers can request personal and sensitive information, such as credit card numbers, and steal it.
|
||||
|
||||
Frequent flushing of the DNS cache will help prevent this from occurring.
|
||||
|
||||
Clearing the DNS cache on your Mac is a relatively straightforward process, even if you don't have a lot of technical knowledge.
|
||||
|
||||
Here is what you will need:
|
||||
|
||||
- Access to the command line,
|
||||
- Your computer password,
|
||||
- To enter a text command (the command will depend on the version of macOS you are running).
|
||||
|
||||
### How to Access The Terminal Application on MacOS
|
||||
|
||||
macOS has a built-in CLI (Command Line Interface) named `Terminal.app`, which allows you to enter text-based commands that the Operating System will carry out.
|
||||
|
||||
There are a few ways to open the terminal.
|
||||
|
||||
The easiest way is through Spotlight search.
|
||||
|
||||
For this, you can:
|
||||
|
||||
- Either navigate to the very top right corner of the screen and click on the icon that looks like a magnifying glass.
|
||||
- Or, you can also use the `Command Space` shortcut.
|
||||
|
||||
Both will open up the following window:
|
||||
|
||||

|
||||
|
||||
From there, start typing `terminal` and click on the `Terminal.app` option that appears.
|
||||
|
||||
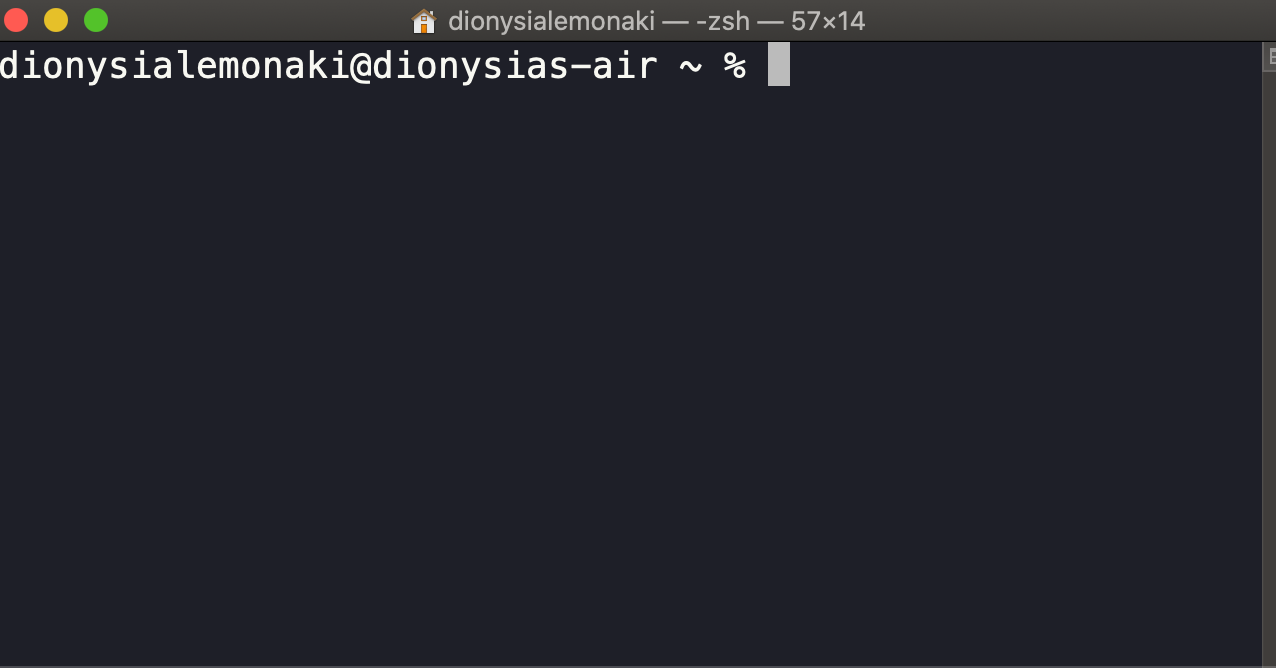
You should see a window open that looks similar to the following:
|
||||
|
||||
|
||||
|
||||
### How to Clear DNS Cache For Your MacOS Version
|
||||
|
||||
In the terminal window, you will then need to enter a command.
|
||||
|
||||
The command is different depending on the version of macOS you are running.
|
||||
|
||||
Each version of macOS has a version number and a version name.
|
||||
|
||||
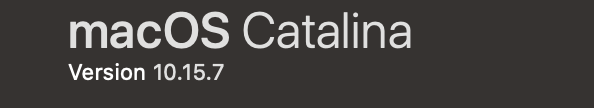
To find out the macOS version on your computer, click on the Apple icon at the very top left corner of your screen. From the dropdown menu that appears, select `About This Mac`.
|
||||
|
||||
In the `Overview` tab, you will first see the version name. Then, underneath that, you will see the version number.
|
||||
|
||||
|
||||
|
||||
In the table below, you will see the versions of macOS in reverse chronological order – from the most recent one to the oldest one.
|
||||
|
||||
Navigate to your version of Mac and copy the respective command.
|
||||
|
||||
| MacOS Version | Command |
|
||||
| --- | --- |
|
||||
| macOS 12 (Monterey) | `sudo dscacheutil -flushcache; sudo killall -HUP mDNSResponder` |
|
||||
| macOS 11 (Big Sur) | `sudo dscacheutil -flushcache; sudo killall -HUP mDNSResponder` |
|
||||
| macOS 10.15 (Catalina) | `sudo dscacheutil -flushcache; sudo killall -HUP mDNSResponder` |
|
||||
| macOS 10.14 (Mojave) | `sudo killall -HUP mDNSResponder` |
|
||||
| macOS 10.13 (High Sierra) | `sudo killall -HUP mDNSResponder` |
|
||||
| macOS 10.12 (Sierra) | `sudo killall -HUP mDNSResponder` |
|
||||
| OS X 10.11 (El Capitan) | `sudo killall -HUP mDNSResponder` |
|
||||
| OS X 10.10 (Yosemite) | `sudo discoveryutil udnsflushcaches` |
|
||||
| OS X 10.9 (Mavericks) | `sudo killall -HUP mDNSResponder` |
|
||||
| OS X 10.8 (Mountain Lion) | `sudo killall -HUP mDNSResponder` |
|
||||
| Mac OS X 10.7 (Lion) | `sudo killall -HUP mDNSResponder` |
|
||||
| Mac OS X 10.6 (Snow Leopard) | `sudo dscacheutil -flushcache` |
|
||||
| Mac OS X 10.5 (Leopard) | `sudo lookupd -flushcache` |
|
||||
| Mac OS X 10.4 (Tiger) | `lookupd -flushcache` |
|
||||
|
||||
After typing the command and hitting enter, there will be a prompt for entering your computer's password.
|
||||
|
||||
Keep in mind that when you are typing your password, you will not be able to view what you are typing – not even any asterisks.
|
||||
|
||||
It appears as though nothing is happening, but rest assured that something is.
|
||||
|
||||
Once you have entered your password and hit enter, you will not see a message indicating that the process is complete.
|
||||
|
||||
Instead, you will view a new terminal prompt.
|
||||
|
||||
## Conclusion
|
||||
|
||||
And there you have it – your local DNS cache is now clear.
|
||||
|
||||
Hopefully, this has helped resolve any connectivity issues you may be experiencing.
|
||||
|
||||
Clearing DNS frequently is always a good idea to help fix troublesome internet connections and ensure your system is secure from potential threats.
|
||||
|
||||
Thanks for reading!
|
||||
|
||||
---
|
||||
|
||||
---
|
||||
|
||||
Learn to code for free. freeCodeCamp's open source curriculum has helped more than 40,000 people get jobs as developers. [Get started](https://www.freecodecamp.org/learn/)
|
||||
@@ -0,0 +1,938 @@
|
||||
---
|
||||
page-title: "MySQL community audit logging - CyberSecThreat"
|
||||
url: https://cybersecthreat.com/2021/12/09/mysql-community-edition-audit-logging/
|
||||
date: "2024-10-25 16:29:56"
|
||||
---
|
||||
|
||||
> Percona audit logging plugin
|
||||
|
||||
---
|
||||
|
||||
## Introduction
|
||||
|
||||
This time, we are going to discuss various options for MySQL community edition authentication audit logging.
|
||||
|
||||
Authentication audit is certainly an important part of continuous monitoring. If a hacker can get the credentials of the database from elsewhere (e.g. compromise of another machine), then the adversary may also be able to directly access the database. Therefore, we may catch attackers earlier using these kinds of IoC.
|
||||
|
||||
### Testing Environments:
|
||||
|
||||
During our research work, we have selected the following 3 environments:
|
||||
|
||||
- `A. Red Hat Enterprise Linux (RHEL) 7.2 & MySQL community server 5.7.19`
|
||||
- `B. Red Hat 7.4 & MySQL community server 5.7.29`
|
||||
- `C. Redhat 8.0 & MySQL community server 8.0.16`
|
||||
|
||||
Before we go in-depth for technical details, we will first list available solutions. However, We will not discuss the MySQL Enterprise audit logging plugin because it only supports MySQL Enterprise.
|
||||
|
||||
- `Native MySQL general_log configuration`
|
||||
- `MySQL Enterprise audit logging plugin (audit_log.so)`
|
||||
- `MariaDB audit logging plugin (server_audit.so)`
|
||||
- `Mcafee audit logging plugin (libaudit_plugin.so)`
|
||||
- `Percona audit logging plugin (audit_log.so)`
|
||||
|
||||
Check out the following compatibility matrix so that you can select the solutions suitable for your environment:
|
||||
|
||||
<table><tbody><tr><td></td><td data-align="center"><strong><code>RHEL 7.2 & MySQL community server 5.7.19</code></strong></td><td data-align="center"><strong><code>RHEL 7.4 & MySQL community server 5.7.29</code></strong></td><td data-align="center"><strong><code>Red Hat 8.0 & MySQL community server 8.0.16</code></strong></td></tr><tr><td><strong><code>Native MySQL general_log configuration</code></strong></td><td data-align="center"><code>✔️</code></td><td data-align="center"><code>✔️</code></td><td data-align="center"><code>✔️</code></td></tr><tr><td><strong><code>MySQL Enterprise audit logging plugin (audit_log.so)</code></strong></td><td data-align="center"><code>❌</code></td><td data-align="center"><code>❌</code></td><td data-align="center"><code>❌</code></td></tr><tr><td><strong><code>MariaDB audit logging plugin (server_audit.so)</code></strong></td><td data-align="center"><code>✔️</code></td><td data-align="center"><code>✔️</code></td><td data-align="center"><code>❌</code></td></tr><tr><td><strong><code>Mcafee audit logging plugin (libaudit_plugin.so)</code></strong></td><td data-align="center"><code>✔️</code></td><td data-align="center"><code>✔️</code></td><td data-align="center"><code>✔️</code></td></tr><tr><td><strong><code>Percona audit logging plugin (audit_log.so)</code></strong></td><td data-align="center"><code>❌</code></td><td data-align="center"><code>❌</code></td><td data-align="center"><code>✔️</code></td></tr></tbody></table>
|
||||
|
||||
Support Matrix for MySQL community authentication logging
|
||||
|
||||
## Description, Pros, and Cons of different MySQL community audit logging:
|
||||
|
||||
### 1\. Native MySQL `general_log` configuration
|
||||
|
||||
- Description
|
||||
- Natively supported by both MySQL community/enterprise version and MariaDB
|
||||
- Logs both authentication and query without the option to filter
|
||||
- Native app by Splunk, but the parsing needs to be fine-tuned.
|
||||
- Pros
|
||||
- Support both MySQL community server 5.7.X and 8.X
|
||||
- Third-party plugin is not needed and therefore no compatibility concerns
|
||||
- Cons
|
||||
- May impact MySQL performance due to it logs ALL query
|
||||
- May raise privacy concern due to SQL statement logged may contain unencrypted sensitive information
|
||||
|
||||
### 2\. MySQL Enterprise audit logging plugin (`audit_log.so`)
|
||||
|
||||
- Description
|
||||
- Introduced since MySQL Enterprise version [5.7.9](https://dev.mysql.com/doc/mysql-security-excerpt/5.7/en/audit-log-reference.html)
|
||||
- Support full auditing as well as only log authentication-related events by using `--audit-log-policy=LOGINS` options.
|
||||
- Pros
|
||||
- Natively comes with MySQL Enterprise edition, thus no compatibility concerns
|
||||
- Cons
|
||||
- Only supports MySQL Enterprise version
|
||||
|
||||
### 3\. MariaDB audit logging plugin (`server_audit.so`)
|
||||
|
||||
- Description
|
||||
- Audit logging plugins developed by MariaDB, which is another company contributed by original founder of MySQL.
|
||||
- Support full auditing as well as only log authentication-related event `server_audit_events='CONNECT'` options
|
||||
- Only supports MySQL community server 5.7.X, but it does not work since MySQL community v5.7.30
|
||||
- Pros
|
||||
- Less compatibility concern because MariaDB 5.5 is completely based on MySQL 5.x
|
||||
- Cons
|
||||
- Additional third-party plugin installation is needed
|
||||
- MySQL community server 8.x is not supported.
|
||||
|
||||
### 4\. Percona audit logging plugin (`audit_log.so`)
|
||||
|
||||
- Description
|
||||
- Audit logging plugins developed by Percona, which is another drop-in replacement of MySQL server.
|
||||
- Support full auditing in different formats (e.g. OLD XML, NEW, JSON, and CSV) as well as only log authentication-related events with `audit_log_policy = LOGINS` options
|
||||
- Only support MySQL community server 8.x
|
||||
- Pros
|
||||
- Less compatibility concern due to Percona 8.0 is based on MySQL 8.0
|
||||
- Cons
|
||||
- Additional third-party plugin installation is required
|
||||
- MySQL community server 5.7 is not supported.
|
||||
|
||||
### 5\. Mcafee audit logging plugin (`libaudit_plugin.so`)
|
||||
|
||||
- Description
|
||||
- Audit logging plugins developed by Mcafee, which has been a CyberSecurity Company for a long time.
|
||||
- Support full auditing in JSON format as well as only log authentication-related events using `audit_record_cmds='connect,Failed Login,Quit'` options
|
||||
- Pros
|
||||
- Support both MySQL community server 5.7.X and 8.X
|
||||
- Cons
|
||||
- Third-party plugin is needed
|
||||
- This may introduce performance impact due to this plugin using non-standard API
|
||||
- Some additional packages (`gdb`, `policycoreutils-devel`) are needed to install
|
||||
- Additional efforts to deal with `SELINUX` settings
|
||||
- Additional effort to deal with process offset using `GDB`
|
||||
- Introduce additional complexity during MySQL upgrade as process offset may change after each MySQL upgrade
|
||||
|
||||
## Conclusion and Recommendation:
|
||||
|
||||
1. In general, we recommend using the MariaDB audit logging plugin for MySQL community 5.7.x, and use Percona audit logging plugin for MySQL community 8.x.
|
||||
2. If you have MySQL community version > 5.7.30, then you can consider both Native MySQL general\_log configuration or Mcafee audit logging plugin.
|
||||
3. If you choose Native MySQL general\_log configuration, then you should consider to encrypt the partition/mount point where logs resides. In addition, check out [our solution](https://cybersecthreat.com/2021/12/09/mysql-community-edition-audit-logging/#native-mysql-general-log-filtering-using-splunk) only includes authentication logs sent to Splunk.
|
||||
|
||||
Although some audit logging plugins support various formats, the configuration format mentioned in this article aligned with our Splunk Apps.
|
||||
|
||||
Since there is no difference between the configuration of ****Redhat 7.****2 ****& MySQL community server 5.7.19**** and **Redhat 7.4 & MySQL community server 5.7.29**, we will list only one here.
|
||||
|
||||
#### **Native logging using general\_log settings**
|
||||
|
||||
Enter MySQL console and show current log settings:
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# mysql -uroot -p -hlocalhost
|
||||
Enter password:
|
||||
Welcome to the MySQL monitor. Commands end with ; or \g.
|
||||
Your MySQL connection id is 2
|
||||
Server version: 5.7.29 MySQL Community Server (GPL)
|
||||
|
||||
Copyright (c) 2000, 2020, Oracle and/or its affiliates. All rights reserved.
|
||||
|
||||
Oracle is a registered trademark of Oracle Corporation and/or its
|
||||
affiliates. Other names may be trademarks of their respective
|
||||
owners.
|
||||
|
||||
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.
|
||||
|
||||
mysql> SHOW VARIABLES LIKE "general_log%";
|
||||
+------------------+-------------------------------+
|
||||
| Variable_name | Value |
|
||||
+------------------+-------------------------------+
|
||||
| general_log | OFF |
|
||||
| general_log_file | /var/lib/mysql/myredhat74.log |
|
||||
+------------------+-------------------------------+
|
||||
2 rows in set (0.00 sec)
|
||||
|
||||
mysql> SHOW VARIABLES LIKE "log_output";
|
||||
+---------------+-------+
|
||||
| Variable_name | Value |
|
||||
+---------------+-------+
|
||||
| log_output | FILE |
|
||||
+---------------+-------+
|
||||
1 row in set (0.00 sec)
|
||||
|
||||
mysql> SHOW VARIABLES LIKE "log_warnings";
|
||||
+---------------+-------+
|
||||
| Variable_name | Value |
|
||||
+---------------+-------+
|
||||
| log_warnings | 2 |
|
||||
+---------------+-------+
|
||||
1 row in set (0.00 sec)
|
||||
|
||||
mysql>
|
||||
```
|
||||
|
||||
While still in MySQL console, we can enable log settings at runtime.
|
||||
|
||||
```
|
||||
mysql> SET global general_log_file='/var/log/mysql/mysql_general.log';
|
||||
Query OK, 0 rows affected (0.00 sec)
|
||||
|
||||
mysql> SET global general_log = on;
|
||||
Query OK, 0 rows affected (0.01 sec)
|
||||
|
||||
mysql> SET global log_output = 'file';
|
||||
Query OK, 0 rows affected (0.00 sec)
|
||||
|
||||
mysql>
|
||||
```
|
||||
|
||||
We will need to edit /etc/my.cnf to enable persistent log settings. The general\_log settings will log all successful and failed attempts as well as queries.
|
||||
|
||||
```
|
||||
[mysqld]
|
||||
general_log = on
|
||||
general_log_file=/var/log/mysql/mysql_general.log
|
||||
```
|
||||
|
||||
It is possible to disable DNS lookups so that MySQL will log source IP addresses instead of hostname. However, you will need to grant permissions using IP addresses rather than a hostname.
|
||||
|
||||
Finally, we will need to create a log directory and restart MySQL daemon.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# mkdir -p /var/log/mysql/
|
||||
[root@myredhat74 ~]# chown -R mysql:mysql /var/log/mysql
|
||||
[root@myredhat74 ~]# systemctl restart mysqld
|
||||
```
|
||||
|
||||
---
|
||||
|
||||
#### MariaDB audit logging plugin (`server_audit.so`) settings
|
||||
|
||||
For MariaDB audit logging plugin, we will need to download the MariaDB binary file and then extract it.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# wget https://downloads.mariadb.org/f/mariadb-5.5.68/bintar-linux-x86_64/mariadb-5.5.68-linux-x86_64.tar.gz/from/http%3A//mirror.mephi.ru/mariadb/?serve -O mariadb-5.5.68-linux-x86_64.tar.gz
|
||||
[root@myredhat74 ~]# tar -zvxf mariadb-5.5.68-linux-x86_64.tar.gz
|
||||
```
|
||||
|
||||
Enter MySQL console and check plugin directory, this directory is default to /usr/lib64/mysql/plugin/ for rpm installation.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# mysql -uroot -p -hlocalhost
|
||||
Enter password:
|
||||
Welcome to the MySQL monitor. Commands end with ; or \g.
|
||||
Your MySQL connection id is 6
|
||||
Server version: 5.7.29 MySQL Community Server (GPL)
|
||||
|
||||
Copyright (c) 2000, 2020, Oracle and/or its affiliates. All rights reserved.
|
||||
|
||||
Oracle is a registered trademark of Oracle Corporation and/or its
|
||||
affiliates. Other names may be trademarks of their respective
|
||||
owners.
|
||||
|
||||
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.
|
||||
|
||||
mysql> SHOW GLOBAL VARIABLES LIKE 'plugin_dir';
|
||||
+---------------+--------------------------+
|
||||
| Variable_name | Value |
|
||||
+---------------+--------------------------+
|
||||
| plugin_dir | /usr/lib64/mysql/plugin/ |
|
||||
+---------------+--------------------------+
|
||||
1 row in set (0.00 sec)
|
||||
|
||||
mysql>
|
||||
```
|
||||
|
||||
After confirming the correct plugin directory, we will need to copy the plugin library to MySQL plugin directory.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# cp ./mariadb-5.5.68-linux-x86_64/lib/plugin/server_audit.so /usr/lib64/mysql/plugin/
|
||||
```
|
||||
|
||||
Enter MySQL console again, and install the plugin.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# mysql -uroot -p -hlocalhost
|
||||
Enter password:
|
||||
Welcome to the MySQL monitor. Commands end with ; or \g.
|
||||
Your MySQL connection id is 5
|
||||
Server version: 5.7.29 MySQL Community Server (GPL)
|
||||
|
||||
Copyright (c) 2000, 2020, Oracle and/or its affiliates. All rights reserved.
|
||||
|
||||
Oracle is a registered trademark of Oracle Corporation and/or its
|
||||
affiliates. Other names may be trademarks of their respective
|
||||
owners.
|
||||
|
||||
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.
|
||||
|
||||
mysql> INSTALL PLUGIN server_audit SONAME 'server_audit.so';
|
||||
Query OK, 0 rows affected (0.02 sec)
|
||||
|
||||
|
||||
mysql> show variables like '%audit%';
|
||||
+-------------------------------+-----------------------+
|
||||
| Variable_name | Value |
|
||||
+-------------------------------+-----------------------+
|
||||
| server_audit_events | |
|
||||
| server_audit_excl_users | |
|
||||
| server_audit_file_path | server_audit.log |
|
||||
| server_audit_file_rotate_now | OFF |
|
||||
| server_audit_file_rotate_size | 1000000 |
|
||||
| server_audit_file_rotations | 9 |
|
||||
| server_audit_incl_users | |
|
||||
| server_audit_loc_info | |
|
||||
| server_audit_logging | OFF |
|
||||
| server_audit_mode | 1 |
|
||||
| server_audit_output_type | file |
|
||||
| server_audit_query_log_limit | 1024 |
|
||||
| server_audit_syslog_facility | LOG_USER |
|
||||
| server_audit_syslog_ident | mysql-server_auditing |
|
||||
| server_audit_syslog_info | |
|
||||
| server_audit_syslog_priority | LOG_INFO |
|
||||
+-------------------------------+-----------------------+
|
||||
|
||||
16 rows in set (0.00 sec)
|
||||
|
||||
mysql>
|
||||
```
|
||||
|
||||
Now, we can add log settings to \[mysqld\] section in my.cnf (or configuration file used by MySQL)
|
||||
|
||||
```
|
||||
server_audit_events='CONNECT'
|
||||
server_audit_logging=on
|
||||
server_audit_file_path = /var/log/mysql/mysql_mariadb_audit.log
|
||||
server_audit_file_rotate_size=200000000
|
||||
server_audit_file_rotations=200
|
||||
server_audit_file_rotate_now=ON
|
||||
```
|
||||
|
||||
Finally, we will need to create a log directory and restart MySQL daemon.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# mkdir -p /var/log/mysql/
|
||||
[root@myredhat74 ~]# chown -R mysql:mysql /var/log/mysql
|
||||
[root@myredhat74 ~]# systemctl restart mysqld
|
||||
```
|
||||
|
||||
Let’s check the final result using Splunk.
|
||||
|
||||
---
|
||||
|
||||
[](https://cybersecthreat.com/wp-content/uploads/2021/12/MySQL_community_audit_logging_for_mariadb_splunk_view.png)
|
||||
|
||||
MySQL community audit logging for MariaDB using Splunk view
|
||||
|
||||
#### **Mcafee audit logging plugin (`libaudit_plugin.so`) settings**
|
||||
|
||||
For Mcafee audit logging plugin, we will need to download the Mcafee binary file and then extract it. Check out the correct version you need here: [https://github.com/mcafee/mysql-audit/releases](https://github.com/mcafee/mysql-audit/releases).
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# wget https://bintray.com/mcafee/mysql-audit-plugin/download_file?file_path=audit-plugin-mysql-5.7-1.1.7-913-linux-x86_64.zip -O audit-plugin-mysql-5.7-1.1.7-913-linux-x86_64.zip
|
||||
[root@myredhat74 ~]# unzip audit-plugin-mysql-5.7-1.1.7-913-linux-x86_64.zip
|
||||
[root@myredhat74 ~]# cp audit-plugin-mysql-5.7-1.1.7-913/lib/libaudit_plugin.so /usr/lib64/mysql/plugin/
|
||||
```
|
||||
|
||||
Check plugin dir, default /usr/lib64/mysql/plugin/ for Enter MySQL console and check plugin directory, this directory is default to /usr/lib64/mysql/plugin/ for rpm installation.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# mysql -uroot -p -hlocalhost
|
||||
Enter password:
|
||||
Welcome to the MySQL monitor. Commands end with ; or \g.
|
||||
Your MySQL connection id is 6
|
||||
Server version: 5.7.29 MySQL Community Server (GPL)
|
||||
|
||||
Copyright (c) 2000, 2020, Oracle and/or its affiliates. All rights reserved.
|
||||
|
||||
Oracle is a registered trademark of Oracle Corporation and/or its
|
||||
affiliates. Other names may be trademarks of their respective
|
||||
owners.
|
||||
|
||||
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.
|
||||
|
||||
mysql> SHOW GLOBAL VARIABLES LIKE 'plugin_dir';
|
||||
+---------------+--------------------------+
|
||||
| Variable_name | Value |
|
||||
+---------------+--------------------------+
|
||||
| plugin_dir | /usr/lib64/mysql/plugin/ |
|
||||
+---------------+--------------------------+
|
||||
1 row in set (0.00 sec)
|
||||
|
||||
mysql>
|
||||
```
|
||||
|
||||
After confirming the correct plugin directory, we will need to copy the plugin library to MySQL plugin directory.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# cp audit-plugin-mysql-5.7-1.1.7-913/lib/libaudit_plugin.so /usr/lib64/mysql/plugin/
|
||||
```
|
||||
|
||||
We also need an extra shell script to get the offset of MySQL binary file.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# wget https://raw.github.com/mcafee/mysql-audit/master/offset-extract/offset-extract.sh
|
||||
[root@myredhat74 ~]# chmod +x offset-extract.sh
|
||||
```
|
||||
|
||||
Then, we can install gdb and run offset-extract.sh to retrieve the offset.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# yum -y install gdb
|
||||
[root@myredhat74 ~]# ./offset-extract.sh /usr/sbin/mysqld
|
||||
//offsets for: /usr/sbin/mysqld (5.7.29)
|
||||
{"5.7.29","00b4b7c8931e964887789044c56346fa", 7824, 7872, 3632, 4792, 456, 360, 0, 32, 64, 160, 536, 7988, 4360, 3648, 3656, 3660, 6072, 2072, 8, 7056, 7096, 7080, 13472, 148, 672, 0},
|
||||
```
|
||||
|
||||
The output from offset-extract.sh is needed under `[mysqld]` section of `my.cnf`.
|
||||
|
||||
```
|
||||
plugin-load=AUDIT=libaudit_plugin.so
|
||||
audit_offsets = 7824, 7872, 3632, 4792, 456, 360, 0, 32, 64, 160, 536, 7988, 4360, 3648, 3656, 3660, 6072, 2072, 8, 7056, 7096, 7080, 13472, 148, 672, 0
|
||||
audit_json_file=1
|
||||
audit_json_log_file=/var/log/mysql/mysql-audit.json
|
||||
audit_record_cmds='connect,Failed Login,Quit'
|
||||
```
|
||||
|
||||
if SELINUX is enabled, then you will need to configure SELINUX Policy as well.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# yum -y install policycoreutils-devel
|
||||
[root@myredhat74 ~]# semanage fcontext -a -t textrel_shlib_t /usr/lib64/mysql/plugin/libaudit_plugin.so
|
||||
[root@myredhat74 ~]# restorecon -v /usr/lib64/mysql/plugin/libaudit_plugin.so
|
||||
[root@myredhat74 ~]# mkdir /root/mcafee-selinux-module
|
||||
[root@myredhat74 ~]# cd /root/mcafee-selinux-module
|
||||
[root@myredhat74 ~]# cat <<EOT >> mysql_libaudit.te
|
||||
|
||||
module mysql_libaudit 1.0;
|
||||
|
||||
require {
|
||||
type mysqld_exec_t;
|
||||
type mysqld_t;
|
||||
class process execmem;
|
||||
class file execmod;
|
||||
}
|
||||
#============= mysqld_t ==============
|
||||
allow mysqld_t mysqld_exec_t:file execmod;
|
||||
allow mysqld_t self:process execmem;
|
||||
EOT
|
||||
[root@myredhat74 ~]# make -f /usr/share/selinux/devel/Makefile
|
||||
[root@myredhat74 ~]# semodule -i mysql_libaudit.pp
|
||||
[root@myredhat74 ~]# cd /root/mcafee-selinux-module
|
||||
[root@myredhat74 ~]# grep mysqld /var/log/audit/audit.log | grep -v lib_t | audit2allow -M mysql_libaudit
|
||||
[root@myredhat74 ~]# semodule -i mysql_libaudit.pp
|
||||
[root@myredhat74 ~]# cd /root
|
||||
[root@myredhat74 ~]# rm -rf /root/mcafee-selinux-module
|
||||
```
|
||||
|
||||
Next, we will need to create a log directory and restart MySQL daemon.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# mkdir -p /var/log/mysql/
|
||||
[root@myredhat74 ~]# chown -R mysql:mysql /var/log/mysql
|
||||
[root@myredhat74 ~]# systemctl restart mysqld
|
||||
```
|
||||
|
||||
Finally, we can check whether the Mcafee Audit library is auto-loaded.
|
||||
|
||||
```
|
||||
[root@myredhat74 ~]# mysql -uroot -p -hlocalhost
|
||||
Enter password:
|
||||
Welcome to the MySQL monitor. Commands end with ; or \g.
|
||||
Your MySQL connection id is 2
|
||||
Server version: 5.7.29 MySQL Community Server (GPL)
|
||||
|
||||
Copyright (c) 2000, 2020, Oracle and/or its affiliates. All rights reserved.
|
||||
|
||||
Oracle is a registered trademark of Oracle Corporation and/or its
|
||||
affiliates. Other names may be trademarks of their respective
|
||||
owners.
|
||||
|
||||
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.
|
||||
|
||||
mysql> show plugins;
|
||||
+----------------------------+----------+--------------------+----------------------+---------+
|
||||
| Name | Status | Type | Library | License |
|
||||
+----------------------------+----------+--------------------+----------------------+---------+
|
||||
| binlog | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| mysql_native_password | ACTIVE | AUTHENTICATION | NULL | GPL |
|
||||
| sha256_password | ACTIVE | AUTHENTICATION | NULL | GPL |
|
||||
| CSV | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| MEMORY | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| InnoDB | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| INNODB_TRX | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_LOCKS | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_LOCK_WAITS | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CMP | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CMP_RESET | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CMPMEM | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CMPMEM_RESET | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CMP_PER_INDEX | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CMP_PER_INDEX_RESET | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_BUFFER_PAGE | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_BUFFER_PAGE_LRU | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_BUFFER_POOL_STATS | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_TEMP_TABLE_INFO | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_METRICS | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_FT_DEFAULT_STOPWORD | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_FT_DELETED | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_FT_BEING_DELETED | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_FT_CONFIG | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_FT_INDEX_CACHE | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_FT_INDEX_TABLE | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_SYS_TABLES | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_SYS_TABLESTATS | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_SYS_INDEXES | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_SYS_COLUMNS | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_SYS_FIELDS | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_SYS_FOREIGN | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_SYS_FOREIGN_COLS | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_SYS_TABLESPACES | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_SYS_DATAFILES | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_SYS_VIRTUAL | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| MyISAM | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| MRG_MYISAM | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| PERFORMANCE_SCHEMA | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| ARCHIVE | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| BLACKHOLE | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| FEDERATED | DISABLED | STORAGE ENGINE | NULL | GPL |
|
||||
| partition | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| ngram | ACTIVE | FTPARSER | NULL | GPL |
|
||||
| AUDIT | ACTIVE | AUDIT | libaudit_plugin.so | GPL |
|
||||
| SERVER_AUDIT | ACTIVE | AUDIT | server_audit.so | GPL |
|
||||
| validate_password | ACTIVE | VALIDATE PASSWORD | validate_password.so | GPL |
|
||||
+----------------------------+----------+--------------------+----------------------+---------+
|
||||
mysql> show global status like 'AUDIT_version';
|
||||
+---------------+-----------+
|
||||
| Variable_name | Value |
|
||||
+---------------+-----------+
|
||||
| Audit_version | 1.1.7-913 |
|
||||
+---------------+-----------+
|
||||
1 row in set (0.00 sec)
|
||||
|
||||
```
|
||||
|
||||
If the library is not auto-loaded, we can enter MySQL console and install the plugin.
|
||||
|
||||
```
|
||||
mysql> INSTALL PLUGIN AUDIT SONAME 'libaudit_plugin.so';
|
||||
```
|
||||
|
||||
Let’s check the final result using Splunk.
|
||||
|
||||
[](https://cybersecthreat.com/wp-content/uploads/2021/12/MySQL_community_audit_logging_for_mcafee_splunk_view.png)
|
||||
|
||||
MySQL community audit logging for Mcafee using Splunk view
|
||||
|
||||
#### **Native logging using `general_log` settings**
|
||||
|
||||
Enter MySQL console and show current log settings:
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# mysql -u root -p -h localhost
|
||||
Enter password:
|
||||
Welcome to the MySQL monitor. Commands end with ; or \g.
|
||||
Your MySQL connection id is 8
|
||||
Server version: 8.0.16 MySQL Community Server - GPL
|
||||
|
||||
Copyright (c) 2000, 2019, Oracle and/or its affiliates. All rights reserved.
|
||||
|
||||
Oracle is a registered trademark of Oracle Corporation and/or its
|
||||
affiliates. Other names may be trademarks of their respective
|
||||
owners.
|
||||
|
||||
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.
|
||||
|
||||
mysql> SHOW VARIABLES LIKE "general_log%";
|
||||
+------------------+------------------------------+
|
||||
| Variable_name | Value |
|
||||
+------------------+------------------------------+
|
||||
| general_log | OFF |
|
||||
| general_log_file | /var/lib/mysql/myredhat8.log |
|
||||
+------------------+------------------------------+
|
||||
2 rows in set (0.01 sec)
|
||||
|
||||
mysql> SHOW VARIABLES LIKE "log_output";
|
||||
+---------------+-------+
|
||||
| Variable_name | Value |
|
||||
+---------------+-------+
|
||||
| log_output | FILE |
|
||||
+---------------+-------+
|
||||
1 row in set (0.00 sec)
|
||||
|
||||
mysql> SHOW VARIABLES LIKE "log_warnings";
|
||||
Empty set (0.00 sec)
|
||||
|
||||
mysql>
|
||||
```
|
||||
|
||||
While still in MySQL console, we can enable log settings at runtime.
|
||||
|
||||
```
|
||||
mysql> SET global general_log_file='/var/log/mysql/mysql_general.log';
|
||||
Query OK, 0 rows affected (0.00 sec)
|
||||
|
||||
mysql> SET global general_log = on;
|
||||
Query OK, 0 rows affected (0.01 sec)
|
||||
|
||||
mysql> SET global log_output = 'file';
|
||||
Query OK, 0 rows affected (0.00 sec)
|
||||
```
|
||||
|
||||
We will need to edit /etc/my.cnf to enable persistent log settings. The general\_log settings will log all successful and failed attempts as well as queries.
|
||||
|
||||
```
|
||||
[mysqld]
|
||||
general_log = on
|
||||
general_log_file=/var/log/mysql/mysql_general.log
|
||||
```
|
||||
|
||||
It is possible to disable DNS lookups so that MySQL will log source IP addresses instead of hostname. However, you will need to grant permissions using IP addresses rather than a hostname.
|
||||
|
||||
Finally, we will need to create a log directory and restart MySQL daemon.
|
||||
|
||||
```
|
||||
mkdir -p /var/log/mysql/
|
||||
chown -R mysql:mysql /var/log/mysql
|
||||
systemctl restart mysqld
|
||||
```
|
||||
|
||||
---
|
||||
|
||||
#### Percona audit logging plugin (`audit_log.so`) settings
|
||||
|
||||
For Percona audit logging plugin, we will need to download the Percona binary file and then extract it.
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# wget https://downloads.percona.com/downloads/Percona-Server-LATEST/Percona-Server-8.0.16-7/binary/redhat/7/x86_64/percona-server-server-8.0.16-7.1.el7.x86_64.rpm
|
||||
[root@myredhat8 ~]# mkdir Percona-Server
|
||||
[root@myredhat8 ~]# mv percona-server-server-8.0.16-7.1.el7.x86_64.rpm Percona-Server/
|
||||
[root@myredhat8 ~]# cd Percona-Server/
|
||||
[root@myredhat8 ~]# rpm2cpio percona-server-server-8.0.16-7.1.el7.x86_64.rpm | cpio -idmv
|
||||
```
|
||||
|
||||
Enter MySQL console and check plugin directory, this directory is default to /usr/lib64/mysql/plugin/ for rpm installation.
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# mysql -u root -p -h localhost
|
||||
Enter password:
|
||||
Welcome to the MySQL monitor. Commands end with ; or \g.
|
||||
Your MySQL connection id is 10
|
||||
Server version: 8.0.16 MySQL Community Server - GPL
|
||||
|
||||
Copyright (c) 2000, 2019, Oracle and/or its affiliates. All rights reserved.
|
||||
|
||||
Oracle is a registered trademark of Oracle Corporation and/or its
|
||||
affiliates. Other names may be trademarks of their respective
|
||||
owners.
|
||||
|
||||
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.
|
||||
|
||||
mysql> SHOW GLOBAL VARIABLES LIKE 'plugin_dir';
|
||||
+---------------+--------------------------+
|
||||
| Variable_name | Value |
|
||||
+---------------+--------------------------+
|
||||
| plugin_dir | /usr/lib64/mysql/plugin/ |
|
||||
+---------------+--------------------------+
|
||||
1 row in set (0.00 sec)
|
||||
|
||||
mysql>
|
||||
```
|
||||
|
||||
After confirming the correct plugin directory, we will need to copy the plugin library to MySQL plugin directory.
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# cp ./usr/lib64/mysql/plugin/audit_log.so /usr/lib64/mysql/plugin/
|
||||
```
|
||||
|
||||
Enter MySQL console again, and install the plugin.
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# mysql -u root -p -h localhost
|
||||
Enter password:
|
||||
Welcome to the MySQL monitor. Commands end with ; or \g.
|
||||
Your MySQL connection id is 9
|
||||
Server version: 8.0.16 MySQL Community Server - GPL
|
||||
|
||||
Copyright (c) 2000, 2019, Oracle and/or its affiliates. All rights reserved.
|
||||
|
||||
Oracle is a registered trademark of Oracle Corporation and/or its
|
||||
affiliates. Other names may be trademarks of their respective
|
||||
owners.
|
||||
|
||||
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.
|
||||
|
||||
|
||||
mysql> INSTALL PLUGIN audit_log SONAME 'audit_log.so';
|
||||
Query OK, 0 rows affected (0.02 sec)
|
||||
```
|
||||
|
||||
Now, we can add log settings to \[mysqld\] section in my.cnf (or configuration file used by MySQL)
|
||||
|
||||
```
|
||||
plugin-load = audit_log.so
|
||||
audit_log_file = /var/log/mysql/audit.log
|
||||
audit_log_format = CSV
|
||||
audit_log_policy = LOGINS
|
||||
audit_log_handler = FILE
|
||||
```
|
||||
|
||||
Finally, we will need to create a log directory and restart MySQL daemon.
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# mkdir -p /var/log/mysql/
|
||||
[root@myredhat8 ~]# chown -R mysql:mysql /var/log/mysql
|
||||
[root@myredhat8 ~]# systemctl restart mysqld
|
||||
```
|
||||
|
||||
Let’s check the final result using Splunk.
|
||||
|
||||
[](https://cybersecthreat.com/wp-content/uploads/2021/12/MySQL_community_audit_logging_for_percona_splunk_view.png)
|
||||
|
||||
MySQL community audit logging for Percona using Splunk view
|
||||
|
||||
---
|
||||
|
||||
#### **Mcafee audit logging plugin (`libaudit_plugin.so`)**
|
||||
|
||||
For Mcafee audit logging plugin, we will need to download the Mcafee binary file and then extract it. Check out the correct version you need here: [https://github.com/mcafee/mysql-audit/releases](https://github.com/mcafee/mysql-audit/releases).
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# wget https://bintray.com/mcafee/mysql-audit-plugin/download_file?file_path=audit-plugin-mysql-8.0-1.1.7-913-linux-x86_64.zip -O audit-plugin-mysql-8.0-1.1.7-913-linux-x86_64.zip
|
||||
[root@myredhat8 ~]# unzip audit-plugin-mysql-8.0-1.1.7-913-linux-x86_64.zip
|
||||
```
|
||||
|
||||
Check plugin dir, default /usr/lib64/mysql/plugin/ for Enter MySQL console and check plugin directory, this directory is default to /usr/lib64/mysql/plugin/ for rpm installation.
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# mysql -u root -p -h localhost
|
||||
Enter password:
|
||||
Welcome to the MySQL monitor. Commands end with ; or \g.
|
||||
Your MySQL connection id is 10
|
||||
Server version: 8.0.16 MySQL Community Server - GPL
|
||||
|
||||
Copyright (c) 2000, 2019, Oracle and/or its affiliates. All rights reserved.
|
||||
|
||||
Oracle is a registered trademark of Oracle Corporation and/or its
|
||||
affiliates. Other names may be trademarks of their respective
|
||||
owners.
|
||||
|
||||
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.
|
||||
|
||||
mysql> SHOW GLOBAL VARIABLES LIKE 'plugin_dir';
|
||||
+---------------+--------------------------+
|
||||
| Variable_name | Value |
|
||||
+---------------+--------------------------+
|
||||
| plugin_dir | /usr/lib64/mysql/plugin/ |
|
||||
+---------------+--------------------------+
|
||||
1 row in set (0.00 sec)
|
||||
|
||||
mysql>
|
||||
```
|
||||
|
||||
After confirming the correct plugin directory, we will need to copy the plugin library to MySQL plugin directory.
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# cp audit-plugin-mysql-8.0-1.1.7-913/lib/libaudit_plugin.so /usr/lib64/mysql/plugin/
|
||||
```
|
||||
|
||||
We also need an extra shell script to get the offset of MySQL binary file.
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# wget https://raw.github.com/mcafee/mysql-audit/master/offset-extract/offset-extract.sh
|
||||
chmod +x offset-extract.sh
|
||||
```
|
||||
|
||||
Then, we can install gdb and run offset-extract.sh to retrieve the offset.
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# yum -y install gdb
|
||||
[root@myredhat8 ~]# ./offset-extract.sh /usr/sbin/mysqld
|
||||
//offsets for: /usr/sbin/mysqld (8.0.16)
|
||||
{"8.0.16","9d238d46151cd5f41fef859c5026f7a0", 8360, 8408, 3912, 5352, 520, 0, 0, 32, 64, 160, 600, 8524, 4984, 4000, 4008, 4012, 6656, 1456, 40, 7616, 7656, 7640, 11416, 140, 664, 328},
|
||||
```
|
||||
|
||||
The output from offset-extract.sh is needed under `[mysqld]` section of `my.cnf`.
|
||||
|
||||
```
|
||||
plugin-load=AUDIT=libaudit_plugin.so
|
||||
audit_offsets = 8360, 8408, 3912, 5352, 520, 0, 0, 32, 64, 160, 600, 8524, 4984, 4000, 4008, 4012, 6656, 1456, 40, 7616, 7656, 7640, 11416, 140, 664, 328
|
||||
audit_json_file=1
|
||||
audit_json_log_file=/var/log/mysql/mysql-audit.json
|
||||
audit_record_cmds='connect,Failed Login,Quit'
|
||||
```
|
||||
|
||||
if SELINUX is enabled, then you will need to configure SELINUX Policy as well.
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# yum -y install policycoreutils-devel
|
||||
[root@myredhat8 ~]# semanage fcontext -a -t textrel_shlib_t
|
||||
/usr/lib64/mysql/plugin/libaudit_plugin.so
|
||||
[root@myredhat8 ~]# restorecon -v /usr/lib64/mysql/plugin/libaudit_plugin.so
|
||||
[root@myredhat8 ~]# mkdir /root/mcafee-selinux-module
|
||||
[root@myredhat8 ~]# cd /root/mcafee-selinux-module
|
||||
[root@myredhat8 ~]# cat <<EOT >> mysql_libaudit.te
|
||||
module mysql_libaudit 1.0;
|
||||
require {
|
||||
type mysqld_t;
|
||||
class process execmem;
|
||||
}
|
||||
|
||||
#============= mysqld_t ==============
|
||||
allow mysqld_t self:process execmem;
|
||||
EOT
|
||||
[root@myredhat8 ~]# make -f /usr/share/selinux/devel/Makefile
|
||||
[root@myredhat8 ~]# semodule -i mysql_libaudit.pp
|
||||
[root@myredhat8 ~]# cd /root/mcafee-selinux-module
|
||||
[root@myredhat8 ~]# grep mysqld /var/log/audit/audit.log | grep -v lib_t | audit2allow -M mysql_libaudit
|
||||
[root@myredhat8 ~]# semodule -i mysql_libaudit.pp
|
||||
[root@myredhat8 ~]# cd /root
|
||||
[root@myredhat8 ~]# rm -rf /root/mcafee-selinux-module
|
||||
```
|
||||
|
||||
Next, we will need to create a log directory and restart MySQL daemon.
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# mkdir -p /var/log/mysql/
|
||||
[root@myredhat8 ~]# chown -R mysql:mysql /var/log/mysql
|
||||
[root@myredhat8 ~]# systemctl restart mysqld
|
||||
```
|
||||
|
||||
Finally, we can check whether the Mcafee Audit library is auto-loaded.
|
||||
|
||||
```
|
||||
[root@myredhat8 ~]# mysql -u root -p -h localhost
|
||||
Enter password:
|
||||
Welcome to the MySQL monitor. Commands end with ; or \g.
|
||||
Your MySQL connection id is 11
|
||||
Server version: 8.0.16 MySQL Community Server - GPL
|
||||
|
||||
Copyright (c) 2000, 2019, Oracle and/or its affiliates. All rights reserved.
|
||||
|
||||
Oracle is a registered trademark of Oracle Corporation and/or its
|
||||
affiliates. Other names may be trademarks of their respective
|
||||
owners.
|
||||
|
||||
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.
|
||||
|
||||
mysql> show plugins;
|
||||
+---------------------------------+----------+--------------------+--------------+---------+
|
||||
| Name | Status | Type | Library | License |
|
||||
+---------------------------------+----------+--------------------+--------------+---------+
|
||||
| binlog | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| mysql_native_password | ACTIVE | AUTHENTICATION | NULL | GPL |
|
||||
| sha256_password | ACTIVE | AUTHENTICATION | NULL | GPL |
|
||||
| caching_sha2_password | ACTIVE | AUTHENTICATION | NULL | GPL |
|
||||
| sha2_cache_cleaner | ACTIVE | AUDIT | NULL | GPL |
|
||||
| CSV | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| MEMORY | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| InnoDB | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| INNODB_TRX | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CMP | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CMP_RESET | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CMPMEM | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CMPMEM_RESET | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CMP_PER_INDEX | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CMP_PER_INDEX_RESET | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_BUFFER_PAGE | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_BUFFER_PAGE_LRU | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_BUFFER_POOL_STATS | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_TEMP_TABLE_INFO | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_METRICS | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_FT_DEFAULT_STOPWORD | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_FT_DELETED | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_FT_BEING_DELETED | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_FT_CONFIG | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_FT_INDEX_CACHE | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_FT_INDEX_TABLE | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_TABLES | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_TABLESTATS | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_INDEXES | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_TABLESPACES | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_COLUMNS | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_VIRTUAL | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_CACHED_INDEXES | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| INNODB_SESSION_TEMP_TABLESPACES | ACTIVE | INFORMATION SCHEMA | NULL | GPL |
|
||||
| MyISAM | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| MRG_MYISAM | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| PERFORMANCE_SCHEMA | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| TempTable | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| ARCHIVE | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| BLACKHOLE | ACTIVE | STORAGE ENGINE | NULL | GPL |
|
||||
| FEDERATED | DISABLED | STORAGE ENGINE | NULL | GPL |
|
||||
| ngram | ACTIVE | FTPARSER | NULL | GPL |
|
||||
| mysqlx | ACTIVE | DAEMON | NULL | GPL |
|
||||
| mysqlx_cache_cleaner | ACTIVE | AUDIT | NULL | GPL |
|
||||
|
|
||||
+---------------------------------+----------+--------------------+--------------+---------+
|
||||
44 rows in set (0.01 sec)
|
||||
|
||||
```
|
||||
|
||||
If the library is not auto-loaded, we can enter MySQL console and install the plugin.
|
||||
|
||||
```
|
||||
mysql> INSTALL PLUGIN AUDIT SONAME 'libaudit_plugin.so';
|
||||
Query OK, 0 rows affected (1.25 sec)
|
||||
|
||||
mysql> show global status like 'AUDIT_version';
|
||||
+---------------+-----------+
|
||||
| Variable_name | Value |
|
||||
+---------------+-----------+
|
||||
| Audit_version | 1.1.7-913 |
|
||||
+---------------+-----------+
|
||||
1 row in set (0.01 sec)
|
||||
|
||||
mysql>
|
||||
```
|
||||
|
||||
Let’s check the final result using Splunk.
|
||||
|
||||
[](https://cybersecthreat.com/wp-content/uploads/2021/12/MySQL_community_audit_logging_for_mcafee_splunk_view.png)
|
||||
|
||||
MySQL community audit logging for Mcafee using Splunk view
|
||||
|
||||
## Native MySQL general\_log filtering using Splunk
|
||||
|
||||
Lastly, we will introduce our solution to filter and only send authentication-related logs to Splunk. In order to simplify things, you can make the below configurations on Splunk universal forwarder, Splunk Heavy Forwarder/Indexer, and Search Head. In addition, you will also need [MySQL Splunk app](https://splunkbase.splunk.com/app/2848/), and ingest MySQL general log using the `sourcetype mysql:generallog:all`.
|
||||
|
||||
Basically, the configuration will first change the sourcetype of authentication logs to mysql:generalQueryLog, and then drop other logs.
|
||||
|
||||
`props.conf`
|
||||
|
||||
```
|
||||
[mysql:generallog:all]
|
||||
# Splunk magic 8 props
|
||||
SHOULD_LINEMERGE = false
|
||||
LINE_BREAKER = ([\r\n]+)
|
||||
TIME_PREFIX = ^
|
||||
MAX_TIMESTAMP_LOOKAHEAD = 27
|
||||
TIME_FORMAT=%Y-%m-%dT%H:%M:%S.%6QZ
|
||||
# 700 is enough for authentication log
|
||||
# TRUNCATE = 700
|
||||
# For_Load_Balancing_On_UF
|
||||
EVENT_BREAKER_ENABLE = true
|
||||
EVENT_BREAKER = ([\r\n]+)
|
||||
|
||||
TRANSFORMS-mysql_generallog = set_mysql_generallog_auth_sourcetype,set_mysql_generallog_nonauth_null
|
||||
|
||||
[mysql:generalQueryLog]
|
||||
EVAL-action = case((Command="Connect" AND like(Argument,"%Access denied for user%")), "failure", (Command="Query" AND Argument=="select @@version_comment limit 1"), "success", true(), null)
|
||||
EVAL-src = client_host
|
||||
EVAL-src_ip = if(cidrmatch("0.0.0.0/0",client_host), client_host, null())
|
||||
```
|
||||
|
||||
`transforms.conf`
|
||||
|
||||
```
|
||||
[set_mysql_generallog_auth_sourcetype]
|
||||
REGEX = (?:^\d{4}-\d{2}-\d{2}T\d{2}:\d{2}:\d{2}.\d{6}Z\s+\d+\s+(?:Query\s+select @@version_comment\s+limit\s+1|Connect\s+.*?@.*))$
|
||||
DEST_KEY = MetaData:Sourcetype
|
||||
FORMAT = sourcetype::mysql:generalQueryLog
|
||||
|
||||
[set_mysql_generallog_nonauth_null]
|
||||
SOURCE_KEY = MetaData:Sourcetype
|
||||
REGEX = mysql:generallog:all
|
||||
DEST_KEY = queue
|
||||
FORMAT = nullQueue
|
||||
```
|
||||
|
||||
Let’s check the final result:
|
||||
|
||||
[](https://cybersecthreat.com/wp-content/uploads/2021/12/MySQL_community_audit_logging_for_generallog_splunk_view.png)
|
||||
|
||||
MySQL community audit logging for generallog using Splunk view
|
||||
|
||||
We have another post about MSSQL monitoring, feel free to visit [here](https://cybersecthreat.com/2020/07/08/enable-mssql-authentication-log-to-eventlog/).
|
||||
|
||||
Reference:
|
||||
|
||||
[https://mariadb.com/kb/en/mariadb-audit-plugin-log-format/](https://mariadb.com/kb/en/mariadb-audit-plugin-log-format/)
|
||||
|
||||
[https://www.percona.com/blog/2020/07/22/percona-audit-log-plugin-and-the-percona-monitoring-and-management-security-threat-tool/](https://www.percona.com/blog/2020/07/22/percona-audit-log-plugin-and-the-percona-monitoring-and-management-security-threat-tool/)
|
||||
@@ -0,0 +1,263 @@
|
||||
---
|
||||
page-title: "技术|我的一些 nix 学习经验:安装和打包"
|
||||
url: https://linux.cn/article-16332-1.html
|
||||
date: "2024-10-25 11:23:58"
|
||||
---
|
||||
最近,我首次尝试了 Mac。直至现在,我注意到的最大缺点是其软件包管理比 Linux 差很多。一段时间以来,我对于 homebrew 感到相当不满,因为每次我安装新的软件包时,它大部分时间都花在了升级上。于是,我萌生了试试 [nix](https://nixos.org/) 包管理器的想法!
|
||||
|
||||
公认的,nix 的使用存在一定困惑性(甚至它有自己单独的编程语言!),因此,我一直在努力以最简洁的方式掌握使用 nix,避开复杂的配置文件管理和新编程语言学习。以下是我至今为止学习到的内容, 敬请期待如何进行:
|
||||
|
||||
- 使用 nix 安装软件包
|
||||
- 为一个名为 [paperjam](https://mj.ucw.cz/sw/paperjam/) 的 C++ 程序构建一个自定义的 nix 包
|
||||
- 用 nix 安装五年前的 [hugo](https://github.com/gohugoio/hugo/) 版本
|
||||
|
||||
如同以往,由于我对 nix 的了解还停留在入门阶段,本篇文章可能存在一些表述不准确的地方。甚至我自己也对于我是否真的喜欢上 nix 感到模棱两可 —— 它的使用真的让人相当困惑!但是,它帮我成功编译了一些以前总是难以编译的软件,并且通常来说,它比 homebrew 的安装速度要快。
|
||||
|
||||
### nix 为何引人关注?
|
||||
|
||||
通常,人们把 nix 定义为一种“声明式的包管理”。尽管我对此并不太感兴趣,但以下是我对 nix 的两个主要欣赏之处:
|
||||
|
||||
- 它提供了二进制包(托管在 [https://cache.nixos.org/](https://cache.nixos.org/) 上),你可以迅速下载并安装
|
||||
- 对于那些没有二进制包的软件,nix 使编译它们变得更容易
|
||||
|
||||
我认为 nix 之所以擅长于编译软件,主要有以下两个原因:
|
||||
|
||||
- 在你的系统中,可以安装同一库或程序的多个版本(例如,你可能有两个不同版本的 libc)。举个例子,我当前的计算机上就存在两个版本的 node,一个位于 `/nix/store/4ykq0lpvmskdlhrvz1j3kwslgc6c7pnv-nodejs-16.17.1`,另一个位于 `/nix/store/5y4bd2r99zhdbir95w5pf51bwfg37bwa-nodejs-18.9.1`。
|
||||
- 除此之外,nix 在构建包时是在隔离的环境下进行的,只使用你明确声明的依赖项的特定版本。因此,你无需担心这个包可能依赖于你的系统里的其它你并不了解的包,再也不用与 `LD_LIBRARY_PATH` 战斗了!许多人投入了大量工作,来列出所有包的依赖项。
|
||||
|
||||
在本文后面,我将给出两个例子,展示 nix 如何使我在编译软件时遇到了更小的困难。
|
||||
|
||||
#### 我是如何开始使用 nix 的
|
||||
|
||||
下面是我开始使用 nix 的步骤:
|
||||
|
||||
- 安装 nix。我忘记了我当时是如何做到这一点,但看起来有一个[官方安装程序](https://nixos.org/download) 和一个来自 [zero-to-nix.com](http://zero-to-nix.com/) 的 [非官方安装程序](https://zero-to-nix.com/concepts/nix-installer)。在 MacOS 上使用标准的多用户安装卸载 nix 的 [教程](https://nixos.org/manual/nix/stable/installation/installing-binary.html#macos) 有点复杂,所以选择一个卸载教程更为简单的安装方法可能值得。
|
||||
- 把 `~/.nix-profile/bin` 添加到我的 `PATH`
|
||||
- 用 `nix-env -iA nixpkgs.NAME` 命令安装包
|
||||
- 就是这样。
|
||||
|
||||
基本上,是把 `nix-env -iA` 当作 `brew install` 或者 `apt-get install`。
|
||||
|
||||
例如,如果我想安装 `fish`,我可以这样做:
|
||||
|
||||
1. `nix-env -iA nixpkgs.fish`
|
||||
|
||||
这看起来就像是从 [https://cache.nixos.org](https://cache.nixos.org/) 下载一些二进制文件 - 非常简单。
|
||||
|
||||
有些人使用 nix 来安装他们的 Node 和 Python 和 Ruby 包,但我并没有那样做 —— 我仍然像我以前一样使用 `npm install` 和 `pip install`。
|
||||
|
||||
#### 一些我没有使用的 nix 功能
|
||||
|
||||
有一些 nix 功能/工具我并没有使用,但我要提及一下。我最初认为你必须使用这些功能才能使用 nix,因为我读过的大部分 nix 教程都讨论了它们。但事实证明,你并不一定要使用它们。
|
||||
|
||||
- NixOS(一个 Linux 发行版)
|
||||
- [nix-shell](https://nixos.org/guides/nix-pills/developing-with-nix-shell.html)
|
||||
- [nix flakes](https://nixos.wiki/wiki/Flakes)
|
||||
- [home-manager](https://github.com/nix-community/home-manager)
|
||||
- [devenv.sh](https://devenv.sh/)
|
||||
|
||||
我不去深入讨论它们,因为我并没真正使用过它们,而且网上已经有很多详解。
|
||||
|
||||
### 安装软件包
|
||||
|
||||
#### nix 包在哪里定义的?
|
||||
|
||||
我认为 nix 包主仓库中的包是定义在 [https://github.com/NixOS/nixpkgs/](https://github.com/NixOS/nixpkgs/)。
|
||||
|
||||
你可以在 [https://search.nixos.org/packages](https://search.nixos.org/packages) 查找包。似乎有两种官方推荐的查找包的方式:
|
||||
|
||||
- `nix-env -qaP NAME`,但这非常缓慢,并且我并没有得到期望的结果
|
||||
- `nix --extra-experimental-features 'nix-command flakes' search nixpkgs NAME`,这倒是管用,但显得有点儿冗长。并且,无论何种原因,它输出的所有包都以 `legacyPackages` 开头
|
||||
|
||||
我找到了一种我更喜欢的从命令行搜索 nix 包的方式:
|
||||
|
||||
- 运行 `nix-env -qa '*' > nix-packages.txt` 获取 Nix 仓库中所有包的列表
|
||||
- 编写一个简洁的 `nix-search` 脚本,仅在 `packages.txt` 中进行 grep 操作(`cat ~/bin/nix-packages.txt | awk '{print $1}' | rg "$1"`)
|
||||
|
||||
#### 所有的东西都是通过符号链接来安装的
|
||||
|
||||
nix 的一个主要设计是,没有一个单一的 `bin` 文件夹来存放所有的包,而是使用了符号链接。有许多层的符号链接。比如,以下就是一些符号链接的例子:
|
||||
|
||||
- 我机器上的 `~/.nix-profile` 最终是一个到 `/nix/var/nix/profiles/per-user/bork/profile-111-link/` 的链接
|
||||
- `~/.nix-profile/bin/fish` 是到 `/nix/store/afkwn6k8p8g97jiqgx9nd26503s35mgi-fish-3.5.1/bin/fish` 的链接
|
||||
|
||||
当我安装某样东西的时候,它会创建一个新的 `profile-112-link` 目录并建立新的链接,并且更新我的 `~/.nix-profile` 使其指向那个目录。
|
||||
|
||||
我认为,这意味着如果我安装了新版本的 `fish` 但我并不满意,我可以很容易地退回先前的版本,只需运行 `nix-env --rollback`,这样就可以让我回到之前的配置文件目录了。
|
||||
|
||||
#### 卸载包并不意味着删除它们
|
||||
|
||||
如果我像这样卸载 nix 包,实际上并不会释放任何硬盘空间,而仅仅是移除了符号链接:
|
||||
|
||||
1. `$ nix-env --uninstall oil`
|
||||
|
||||
我尚不清楚如何彻底删除包 - 我试着运行了如下的垃圾收集命令,这似乎删除了一些项目:
|
||||
|
||||
1. `$ nix-collect-garbage`
|
||||
2. `...`
|
||||
3. `85 store paths deleted, 74.90 MiB freed`
|
||||
|
||||
然而,我系统上仍然存在 `oil` 包,在 `/nix/store/8pjnk6jr54z77jiq5g2dbx8887dnxbda-oil-0.14.0`。
|
||||
|
||||
`nix-collect-garbage` 有一个更具攻击性的版本,它也会删除你配置文件的旧版本(这样你就不能回滚了)。
|
||||
|
||||
1. `$ nix-collect-garbage -d --delete-old`
|
||||
|
||||
尽管如此,上述命令仍无法删除 `/nix/store/8pjnk6jr54z77jiq5g2dbx8887dnxbda-oil-0.14.0`,我不明白原因。
|
||||
|
||||
#### 升级过程
|
||||
|
||||
你可以通过以下的方式升级 nix 包:
|
||||
|
||||
1. `nix-channel --update`
|
||||
2. `nix-env --upgrade`
|
||||
|
||||
(这与 `apt-get update && apt-get upgrade` 类似。)
|
||||
|
||||
我还没真正尝试升级任何东西。我推测,如果升级过程中出现任何问题,我可以通过以下方式轻松地回滚(因为在 nix 中,所有事物都是不可变的!):
|
||||
|
||||
1. `nix-env --rollback`
|
||||
|
||||
有人向我推荐了 Ian Henry 的 [这篇文章](https://ianthehenry.com/posts/how-to-learn-nix/my-first-package-upgrade/),该文章讨论了 `nix-env --upgrade` 的一些令人困惑的问题 - 也许它并不总是如我们所料?因此,我会对升级保持警惕。
|
||||
|
||||
### 下一个目标:创建名为 paperjam 的自定义包
|
||||
|
||||
经过几个月使用现有的 nix 包后,我开始考虑制作自定义包,对象是一个名为 [paperjam](https://mj.ucw.cz/sw/paperjam/) 的程序,它还没有被打包封装。
|
||||
|
||||
实际上,因为我系统上的 `libiconv` 版本不正确,我甚至在没有 nix 的情况下也遇到了编译 `paperjam` 的困难。我认为,尽管我还不懂如何制作 nix 包,但使用 nix 来编译它可能会更为简单。结果证明我的想法是对的!
|
||||
|
||||
然而,理清如何实现这个目标的过程相当复杂,因此我在这里写下了一些我实现它的方式和步骤。
|
||||
|
||||
#### 构建示例包的步骤
|
||||
|
||||
在我着手制作 `paperjam` 自定义包之前,我想先试手构建一个已存在的示例包,以便确保我已经理解了构建包的整个流程。这个任务曾令我头痛不已,但在我在 Discord 提问之后,有人向我阐述了如何从 [https://github.com/NixOS/nixpkgs/](https://github.com/NixOS/nixpkgs/) 获取一个可执行的包并进行构建。以下是操作步骤:
|
||||
|
||||
**步骤 1:** 从 GitHub 的 [nixpkgs](https://github.com/NixOS/nixpkgs/) 下载任意一个包,以 `dash` 包为例:
|
||||
|
||||
1. `wget https://raw.githubusercontent.com/NixOS/nixpkgs/47993510dcb7713a29591517cb6ce682cc40f0ca/pkgs/shells/dash/default.nix -O dash.nix`
|
||||
|
||||
**步骤 2:** 用 `with import <nixpkgs> {};` 替换开头的声明(`{ lib , stdenv , buildPackages , autoreconfHook , pkg-config , fetchurl , fetchpatch , libedit , runCommand , dash }:`)。我不清楚为何需要这样做,但事实证明这么做是有效的。
|
||||
|
||||
**步骤 3:** 运行 `nix-build dash.nix`
|
||||
|
||||
这将开始编译该包。
|
||||
|
||||
**步骤 4:** 运行 `nix-env -i -f dash.nix`
|
||||
|
||||
这会将该包安装到我的 `~/.nix-profile` 目录下。
|
||||
|
||||
就这么简单!一旦我完成了这些步骤,我便感觉自己能够逐步修改 `dash` 包,进一步创建属于我自己的包了。
|
||||
|
||||
#### 制作自定义包的过程
|
||||
|
||||
因为 `paperjam` 依赖于 `libpaper`,而 `libpaper` 还没有打包,所以我首先需要构建 `libpaper` 包。
|
||||
|
||||
以下是 `libpaper.nix`,我基本上是从 [nixpkgs](https://github.com/NixOS/nixpkgs/) 仓库中其他包的源码中复制粘贴得到的。我猜测这里的原理是,nix 对如何编译 C 包有一些默认规则,例如 “运行 `make install`”,所以 `make install` 实际上是默认执行的,并且我并不需要明确地去配置它。
|
||||
|
||||
1. `with import <nixpkgs> {};`
|
||||
|
||||
3. `stdenv.mkDerivation rec {`
|
||||
4. `pname = "libpaper";`
|
||||
5. `version = "0.1";`
|
||||
|
||||
7. `src = fetchFromGitHub {`
|
||||
8. `owner = "naota";`
|
||||
9. `repo = "libpaper";`
|
||||
10. `rev = "51ca11ec543f2828672d15e4e77b92619b497ccd";`
|
||||
11. `hash = "sha256-S1pzVQ/ceNsx0vGmzdDWw2TjPVLiRgzR4edFblWsekY=";`
|
||||
12. `};`
|
||||
|
||||
14. `buildInputs = [ ];`
|
||||
|
||||
16. `meta = with lib; {`
|
||||
17. `homepage = "https://github.com/naota/libpaper";`
|
||||
18. `description = "libpaper";`
|
||||
19. `platforms = platforms.unix;`
|
||||
20. `license = with licenses; [ bsd3 gpl2 ];`
|
||||
21. `};`
|
||||
22. `}`
|
||||
|
||||
这个脚本基本上告诉 nix 如何从 GitHub 下载源代码。
|
||||
|
||||
我通过运行 `nix-build libpaper.nix` 来构建它。
|
||||
|
||||
接下来,我需要编译 `paperjam`。我制作的 [nix 包](https://github.com/jvns/nixpkgs/blob/22b70a48a797538c76b04261b3043165896d8f69/paperjam.nix) 的链接在这里。除了告诉它从哪里下载源码外,我需要做的主要事情有:
|
||||
|
||||
- 添加一些额外的构建依赖项(像 `asciidoc`)
|
||||
- 在安装过程中设置一些环境变量(`installFlags = [ "PREFIX=$(out)" ];`),这样它就会被安装在正确的目录,而不是 `/usr/local/bin`。
|
||||
|
||||
我首先从散列值为空开始,然后运行 `nix-build` 以获取一个关于散列值不匹配的错误信息。然后我从错误信息中复制出正确的散列值。
|
||||
|
||||
我只是在 nixpkgs 仓库中运行 `rg PREFIX` 来找出如何设置 `installFlags` 的 —— 我认为设置 `PREFIX` 应该是很常见的操作,可能之前已经有人做过了,事实证明我的想法是对的。所以我只是从其他包中复制粘贴了那部分代码。
|
||||
|
||||
然后我执行了:
|
||||
|
||||
1. `nix-build paperjam.nix`
|
||||
2. `nix-env -i -f paperjam.nix`
|
||||
|
||||
然后所有的东西都开始工作了,我成功地安装了 `paperjam`!耶!
|
||||
|
||||
### 下一个目标:安装一个五年前的 Hugo 版本
|
||||
|
||||
当前,我使用的是 2018 年的 Hugo 0.40 版本来构建我的博客。由于我并不需要任何的新功能,因此我并没有感到有升级的必要。对于在 Linux 上操作,这个过程非常简单:Hugo 的发行版本是静态二进制文件,这意味着我可以直接从 [发布页面](https://github.com/gohugoio/hugo/releases/tag/v0.40) 下载五年前的二进制文件并运行。真的很方便!
|
||||
|
||||
但在我的 Mac 电脑上,我遇到了一些复杂的情况。过去五年中,Mac 的硬件已经发生了一些变化,因此我下载的 Mac 版 Hugo 二进制文件并不能运行。同时,我尝试使用 `go build` 从源代码编译,但由于在过去的五年内 Go 的构建规则也有所改变,因此没有成功。
|
||||
|
||||
我曾试图通过在 Linux docker 容器中运行 Hugo 来解决这个问题,但我并不太喜欢这个方法:尽管可以工作,但它运行得有些慢,而且我个人感觉这样做有些多余。毕竟,编译一个 Go 程序不应该那么麻烦!
|
||||
|
||||
幸好,Nix 来救援!接下来,我将介绍我是如何使用 nix 来安装旧版本的 Hugo。
|
||||
|
||||
#### 使用 nix 安装 Hugo 0.40 版本
|
||||
|
||||
我的目标是安装 Hugo 0.40,并将其添加到我的 PATH 中,以 `hugo-0.40` 作为命名。以下是我实现此目标的步骤。尽管我采取了一种相对特殊的方式进行操作,但是效果不错(可以参考 [搜索和安装旧版本的 Nix 包](https://lazamar.github.io/download-specific-package-version-with-nix/) 来找到可能更常规的方法)。
|
||||
|
||||
**步骤 1:** 在 nixpkgs 仓库中搜索找到 Hugo 0.40。
|
||||
|
||||
我在此链接中找到了相应的 `.nix` 文件 [https://github.com/NixOS/nixpkgs/blob/17b2ef2/pkgs/applications/misc/hugo/default.nix](https://github.com/NixOS/nixpkgs/blob/17b2ef2/pkgs/applications/misc/hugo/default.nix)。
|
||||
|
||||
**步骤 2:** 下载该文件并进行构建。
|
||||
|
||||
我下载了带有 `.nix` 扩展名的文件(以及同一目录下的另一个名为 `deps.nix` 的文件),将文件的首行替换为 `with import <nixpkgs> {};`,然后使用 `nix-build hugo.nix` 进行构建。
|
||||
|
||||
虽然这个过程几乎无需进行修改就能成功运行,但我仍然做了两处小调整:
|
||||
|
||||
- 把 `with stdenv.lib` 替换为 `with lib`。
|
||||
- 为避免与我已安装的其他版本的 `hugo` 冲突,我把包名改为了 `hugo040`。
|
||||
|
||||
**步骤 3:** 将 `hugo` 重命名为 `hugo-0.40`。
|
||||
|
||||
我编写了一个简短的后安装脚本,用以重命名 Hugo 二进制文件。
|
||||
|
||||
1. `postInstall = ''`
|
||||
2. `mv $out/bin/hugo $out/bin/hugo-0.40`
|
||||
3. `'';`
|
||||
|
||||
我是通过在 nixpkgs 仓库中运行 `rg 'mv '` 命令,然后复制和修改一条看似相关的代码片段来找到如何实施此步骤。
|
||||
|
||||
**步骤 4:** 安装。
|
||||
|
||||
我通过运行 `nix-env -i -f hugo.nix` 命令,将 Hugo 安装到了 `~/.nix-profile/bin` 目录中。
|
||||
|
||||
所有的步骤都顺利运行了!我把最终的 `.nix` 文件存放到了我自己的 [nixpkgs 仓库](https://github.com/jvns/nixpkgs/) 中,这样我以后如果需要,就能再次使用它了。
|
||||
|
||||
### 可重复的构建过程并非神秘,其实它们极其复杂
|
||||
|
||||
我觉得值得一提的是,这个 `hugo.nix` 文件并不是什么魔法——我之所以能在今天轻易地编译 Hugo 0.40,完全归功于许多人长期以来的付出,他们让 Hugo 的这个版本得以以可重复的方式打包。
|
||||
|
||||
### 总结
|
||||
|
||||
安装 `paperjam` 和这个五年前的 Hugo 版本过程惊人地顺利,实际上比没有 nix 来编译它们更简单。这是因为 nix 极大地方便了我使用正确的 `libiconv` 版本来编译 `paperjam` 包,而且五年前就已经有人辛苦地列出了 Hugo 的确切依赖关系。
|
||||
|
||||
我并无计划详细深入地使用 nix(真的,我很可能对它感到困扰,然后最后选择回归使用 homebrew!),但我们将拭目以待!我发现,简单入手然后按需逐步掌握更多功能,远比一开始就全面接触一堆复杂功能更容易掌握。
|
||||
|
||||
我可能不会在 Linux 上使用 nix —— 我一直都对 Debian 基础发行版的 `apt` 和 Arch 基础发行版的 `pacman` 感到满意,它们策略明晰且少有混淆。而在 Mac 上,使用 nix 似乎会有所得。不过,谁知道呢!也许三个月后,我可能会对 nix 感到不满然后再次选择回归使用 homebrew。
|
||||
|
||||
*(题图:MJ/f68aaf37-4a34-4643-b3a1-8728d49cf887)*
|
||||
|
||||
---
|
||||
|
||||
via: [https://jvns.ca/blog/2023/02/28/some-notes-on-using-nix/](https://jvns.ca/blog/2023/02/28/some-notes-on-using-nix/)
|
||||
|
||||
作者:[Julia Evans](https://jvns.ca/) 选题:[lkxed](https://github.com/lkxed/) 译者:[ChatGPT](https://linux.cn/lctt/ChatGPT) 校对:[wxy](https://github.com/wxy)
|
||||
|
||||
本文由 [LCTT](https://github.com/LCTT/TranslateProject) 原创编译,[Linux中国](https://linux.cn/article-16332-1.html) 荣誉推出
|
||||
@@ -0,0 +1,209 @@
|
||||
---
|
||||
page-title: "权限校验 | Nacos 官网"
|
||||
url: https://nacos.io/docs/latest/guide/user/auth/
|
||||
date: "2024-10-31 15:59:17"
|
||||
---
|
||||
> 该文档即将废弃,若想查看服务端如何开启鉴权功能推荐查看[运维手册-鉴权手册](https://nacos.io/docs/latest/manual/admin/auth/); 若想查看客户端如何配置鉴权信息推荐查看[用户手册-配置鉴权信息](https://nacos.io/docs/latest/manual/user/auth/)。
|
||||
|
||||
> 注意
|
||||
>
|
||||
> - Nacos是一个内部微服务组件,需要在可信的内部网络中运行,不可暴露在公网环境,防止带来安全风险。
|
||||
> - Nacos提供简单的鉴权实现,为防止业务错用的弱鉴权体系,不是防止恶意攻击的强鉴权体系。
|
||||
> - 如果运行在不可信的网络环境或者有强鉴权诉求,请参考官方简单实现做进行[自定义插件开发](https://nacos.io/docs/latest/plugin/auth-plugin/)。
|
||||
|
||||
## 鉴权
|
||||
|
||||
## 相关参数
|
||||
|
||||
| 参数名 | 默认值 | 启止版本 | 说明 |
|
||||
| --- | --- | --- | --- |
|
||||
| nacos.core.auth.enabled | false | 1.2.0 ~ latest | 是否开启鉴权功能 |
|
||||
| nacos.core.auth.system.type | nacos | 1.2.0 ~ latest | 鉴权类型 |
|
||||
| nacos.core.auth.plugin.nacos.token.secret.key | SecretKey012345678901234567890123456789012345678901234567890123456789(2.2.0.1后无默认值) | 2.1.0 ~ latest | 默认鉴权插件用于生成用户登陆临时accessToken所使用的密钥,**使用默认值有安全风险** |
|
||||
| nacos.core.auth.plugin.nacos.token.expire.seconds | 18000 | 2.1.0 ~ latest | 用户登陆临时accessToken的过期时间 |
|
||||
| nacos.core.auth.enable.userAgentAuthWhite | false | 1.4.1 ~ latest | 是否使用useragent白名单,主要用于适配老版本升级,**置为true时有安全风险** |
|
||||
| nacos.core.auth.server.identity.key | serverIdentity(2.2.1后无默认值) | 1.4.1 ~ latest | 用于替换useragent白名单的身份识别key,**使用默认值有安全风险** |
|
||||
| nacos.core.auth.server.identity.value | security(2.2.1后无默认值) | 1.4.1 ~ latest | 用于替换useragent白名单的身份识别value,**使用默认值有安全风险** |
|
||||
| ~nacos.core.auth.default.token.secret.key~ | SecretKey012345678901234567890123456789012345678901234567890123456789 | 1.2.0 ~ 2.0.4 | 同`nacos.core.auth.plugin.nacos.token.secret.key` |
|
||||
| ~nacos.core.auth.default.token.expire.seconds~ | 18000 | 1.2.0 ~ 2.0.4 | 同`nacos.core.auth.plugin.nacos.token.expire.seconds` |
|
||||
|
||||
## 默认控制台登录页
|
||||
|
||||
2.2.2版本之前的Nacos默认控制台,无论服务端是否开启鉴权,都会存在一个登录页;这导致很多用户被**误导**认为Nacos默认是存在鉴权的。在社区安全工程师的建议下,Nacos自**2.2.2**版本开始,在未开启鉴权时,默认控制台将不需要登录即可访问,同时在控制台中给予提示,提醒用户当前集群未开启鉴权。
|
||||
|
||||
在用户开启鉴权后,控制台才需要进行登录访问。 同时针对不同的鉴权插件,提供新的接口方法,用于提示控制台是否开启登录页;同时在`2.2.3`版本后,Nacos可支持关闭开源控制台,并引导到用户自定义的Nacos控制台,详情可查看[Nacos鉴权插件-服务端插件](https://nacos.io/docs/latest/plugin/auth-plugin/)及[控制台手册-关闭登录功能](https://nacos.io/docs/latest/guide/admin/console-guide/#1.1)
|
||||
|
||||
## 服务端如何开启鉴权
|
||||
|
||||
### 非Docker环境
|
||||
|
||||
按照官方文档配置启动,默认是不需要登录的,这样会导致配置中心对外直接暴露。而启用鉴权之后,需要在使用用户名和密码登录之后,才能正常使用nacos。
|
||||
|
||||
开启鉴权之前,application.properties中的配置信息为:
|
||||
|
||||
```
|
||||
### If turn on auth system:nacos.core.auth.enabled=false
|
||||
```
|
||||
|
||||
开启鉴权之后,application.properties中的配置信息为:
|
||||
|
||||
```
|
||||
### If turn on auth system:nacos.core.auth.system.type=nacosnacos.core.auth.enabled=true
|
||||
```
|
||||
|
||||
#### 自定义密钥
|
||||
|
||||
开启鉴权之后,你可以自定义用于生成JWT令牌的密钥,application.properties中的配置信息为:
|
||||
|
||||
> 注意:
|
||||
>
|
||||
> 1. 文档中提供的密钥为公开密钥,在实际部署时请更换为其他密钥内容,防止密钥泄漏导致安全风险。
|
||||
> 2. 在2.2.0.1版本后,社区发布版本将移除以文档如下值作为默认值,需要自行填充,否则无法启动节点。
|
||||
> 3. 密钥需要保持节点间一致,长时间不一致可能导致403 invalid token错误。
|
||||
|
||||
```
|
||||
### The default token(Base64 String):nacos.core.auth.default.token.secret.key=SecretKey012345678901234567890123456789012345678901234567890123456789### 2.1.0 版本后nacos.core.auth.plugin.nacos.token.secret.key=SecretKey012345678901234567890123456789012345678901234567890123456789
|
||||
```
|
||||
|
||||
自定义密钥时,推荐将配置项设置为**Base64编码**的字符串,且**原始密钥长度不得低于32字符**。例如下面的的例子:
|
||||
|
||||
```
|
||||
### The default token(Base64 String):nacos.core.auth.default.token.secret.key=VGhpc0lzTXlDdXN0b21TZWNyZXRLZXkwMTIzNDU2Nzg=### 2.1.0 版本后nacos.core.auth.plugin.nacos.token.secret.key=VGhpc0lzTXlDdXN0b21TZWNyZXRLZXkwMTIzNDU2Nzg=
|
||||
```
|
||||
|
||||
> 注意:鉴权开关是修改之后立马生效的,不需要重启服务端。动态修改`token.secret.key`时,请确保token是有效的,如果修改成无效值,会导致后续无法登录,请求访问异常。
|
||||
|
||||
### Docker环境
|
||||
|
||||
#### 官方镜像
|
||||
|
||||
如果使用官方镜像,请在启动docker容器时,添加如下环境变量
|
||||
|
||||
例如,可以通过如下命令运行开启了鉴权的容器:
|
||||
|
||||
```
|
||||
docker run --env PREFER_HOST_MODE=hostname \ --env MODE=standalone \ --env NACOS_AUTH_ENABLE=true \ -e NACOS_AUTH_TOKEN=SecretKeyM1Z2WDc4dnVyZkQ3NmZMZjZ3RHRwZnJjNFROdkJOemEK \ -e NACOS_AUTH_IDENTITY_KEY=mpYGXyu7 \ -e NACOS_AUTH_IDENTITY_VALUE=mpYGXyu7 \ -p 8848:8848 nacos/nacos-server
|
||||
```
|
||||
|
||||
除此之外,还可以添加其他鉴权相关的环境变量信息:
|
||||
|
||||
| name | description | option |
|
||||
| --- | --- | --- |
|
||||
| NACOS\_AUTH\_ENABLE | 是否开启权限系统 | 默认 |
|
||||
| NACOS\_AUTH\_TOKEN\_EXPIRE\_SECONDS | token 失效时间 | 默认:18000 |
|
||||
| NACOS\_AUTH\_TOKEN | token | 默认 |
|
||||
| NACOS\_AUTH\_CACHE\_ENABLE | 权限缓存开关 ,开启后权限缓存的更新默认有15秒的延迟 | 默认 : false |
|
||||
|
||||
然后运行docker-compose构建命令,例如
|
||||
|
||||
```
|
||||
docker-compose -f example/standalone-derby.yaml up
|
||||
```
|
||||
|
||||
#### 自定义镜像
|
||||
|
||||
如果选择自定义镜像,请在构建镜像之前,修改nacos工程中的application.properties文件,
|
||||
|
||||
将下面这一行配置信息
|
||||
|
||||
```
|
||||
nacos.core.auth.enabled=false
|
||||
```
|
||||
|
||||
修改为
|
||||
|
||||
```
|
||||
nacos.core.auth.system.type=nacosnacos.core.auth.enabled=true
|
||||
```
|
||||
|
||||
然后再配置nacos启动命令。
|
||||
|
||||
## 客户端如何进行鉴权
|
||||
|
||||
### Java SDK鉴权
|
||||
|
||||
在构建“Properties”类时,需传入用户名和密码。
|
||||
|
||||
```
|
||||
properties.put("username","${username}");properties.put("password","${password}");
|
||||
```
|
||||
|
||||
#### 示例代码
|
||||
|
||||
```
|
||||
try { // Initialize the configuration service, and the console automatically obtains the following parameters through the sample code. String serverAddr = "{serverAddr}"; Properties properties = new Properties(); properties.put("serverAddr", serverAddr); // if need username and password to login properties.put("username","nacos"); properties.put("password","nacos"); ConfigService configService = NacosFactory.createConfigService(properties);} catch (NacosException e) { // TODO Auto-generated catch block e.printStackTrace();}
|
||||
```
|
||||
|
||||
### 其他语言的SDK鉴权
|
||||
|
||||
待补充
|
||||
|
||||
### Open-API鉴权
|
||||
|
||||
首先需要使用用户名和密码登陆nacos。
|
||||
|
||||
```
|
||||
curl -X POST '127.0.0.1:8848/nacos/v1/auth/login' -d 'username=nacos&password=nacos'
|
||||
```
|
||||
|
||||
若用户名和密码正确,返回信息如下:
|
||||
|
||||
```
|
||||
{"accessToken":"eyJhbGciOiJIUzI1NiJ9.eyJzdWIiOiJuYWNvcyIsImV4cCI6MTYwNTYyOTE2Nn0.2TogGhhr11_vLEjqKko1HJHUJEmsPuCxkur-CfNojDo","tokenTtl":18000,"globalAdmin":true}
|
||||
```
|
||||
|
||||
接下来进行配置信息或服务信息时,应当使用该accessToken鉴权,在url后添加参数accessToken=${accessToken},其中${accessToken}为登录时返回的token信息,例如
|
||||
|
||||
```
|
||||
curl -X GET '127.0.0.1:8848/nacos/v1/cs/configs?accessToken=eyJhbGciOiJIUzI1NiJ9.eyJzdWIiOiJuYWNvcyIsImV4cCI6MTYwNTYyMzkyM30.O-s2yWfDSUZ7Svd3Vs7jy9tsfDNHs1SuebJB4KlNY8Q&dataId=nacos.example.1&group=nacos_group'
|
||||
```
|
||||
|
||||
```
|
||||
curl -X POST 'http://127.0.0.1:8848/nacos/v1/ns/instance?accessToken=eyJhbGciOiJIUzI1NiJ9.eyJzdWIiOiJuYWNvcyIsImV4cCI6MTYwNTYyMzkyM30.O-s2yWfDSUZ7Svd3Vs7jy9tsfDNHs1SuebJB4KlNY8Q&port=8848&healthy=true&ip=11.11.11.11&weight=1.0&serviceName=nacos.test.3&encoding=GBK&namespaceId=n1'
|
||||
```
|
||||
|
||||
## 开启Token缓存功能
|
||||
|
||||
服务端自2.2.1版本后,默认鉴权插件模块支持token缓存功能,可参见ISSUE #9906
|
||||
|
||||
```
|
||||
https://github.com/alibaba/nacos/issues/9906
|
||||
```
|
||||
|
||||
#### 背景
|
||||
|
||||
无论是客户端SDK还是OpenAPI,在调用login接口获取accessToken之后,携带accessToken访问服务端,服务端解析Token进行鉴权。解析的动作比较耗时,如果想要提升接口的性能,可以考虑开启缓存Token的功能,用字符串比较代替Token解析。
|
||||
|
||||
#### 开启方式
|
||||
|
||||
```
|
||||
nacos.core.auth.plugin.nacos.token.cache.enable=true
|
||||
```
|
||||
|
||||
#### 注意事项
|
||||
|
||||
在开启Token缓存功能之前,服务端对每一个携带用户名密码访问login接口的请求都会生成新的token,接口的返回值中的tokenTtl字段跟服务端配置文件中设置的值相等,配置如下:
|
||||
|
||||
```
|
||||
nacos.core.auth.plugin.nacos.token.expire.seconds=18000
|
||||
```
|
||||
|
||||
在开启Token缓存功能之后,服务端对每一个携带用户名密码访问login接口的请求,会先检查缓存中是否存在该用户名对应的token。若不存在,生成新的Token,插入缓存再返回;若存在,返回该token,此时tokenTtl字段的值为配置文件中设置的值减去该Token在缓存中存留的时长。 如果Token在缓存中存留的时长超过配置文件设置的值的90%,当login接口收到请求时,尽管缓存中存在该用户名对应的Token,服务端会重新生成Token返回给请求方,并更新缓存。因此,最差情况下,请求方收到的tokenTtl只有配置文件设置的值的10%。
|
||||
|
||||
## 开启服务身份识别功能
|
||||
|
||||
开启鉴权功能后,服务端之间的请求也会通过鉴权系统的影响。考虑到服务端之间的通信应该是可信的,因此在1.2~1.4.0版本期间,通过User-Agent中是否包含Nacos-Server来进行判断请求是否来自其他服务端。
|
||||
|
||||
但这种实现由于过于简单且固定,导致可能存在安全问题。因此从1.4.1版本开始,Nacos添加服务身份识别功能,用户可以自行配置服务端的Identity,不再使用User-Agent作为服务端请求的判断标准。
|
||||
|
||||
开启方式:
|
||||
|
||||
```
|
||||
### 开启鉴权nacos.core.auth.enabled=true### 关闭使用user-agent判断服务端请求并放行鉴权的功能nacos.core.auth.enable.userAgentAuthWhite=false### 配置自定义身份识别的key(不可为空)和value(不可为空)nacos.core.auth.server.identity.key=examplenacos.core.auth.server.identity.value=example
|
||||
```
|
||||
|
||||
\*\* 注意 \*\* 所有集群均需要配置相同的`server.identity`信息,否则可能导致服务端之间数据不一致或无法删除实例等问题。
|
||||
|
||||
### 旧版本升级
|
||||
|
||||
考虑到旧版本用户需要升级,可以在升级期间,开启`nacos.core.auth.enable.userAgentAuthWhite=true`功能,待集群整体升级到1.4.1并稳定运行后,再关闭此功能。
|
||||
Reference in New Issue
Block a user