vault backup: 2026-01-05 13:03:55
This commit is contained in:
 windyboy
@@ -0,0 +1,58 @@
|
||||
---
|
||||
page-title: "Creating user accounts | Dendrite"
|
||||
url: https://matrix-org.github.io/dendrite/administration/createusers
|
||||
date: "2023-05-06 10:35:52"
|
||||
---
|
||||
## [](https://matrix-org.github.io/dendrite/administration/createusers#creating-user-accounts)Creating user accounts
|
||||
|
||||
User accounts can be created on a Dendrite instance in a number of ways.
|
||||
|
||||
## [](https://matrix-org.github.io/dendrite/administration/createusers#from-the-command-line)From the command line
|
||||
|
||||
The `create-account` tool is built in the `bin` folder when building Dendrite with the `build.sh` script.
|
||||
|
||||
It uses the `dendrite.yaml` configuration file to connect to a running Dendrite instance and requires shared secret registration to be enabled as explained below.
|
||||
|
||||
An example of using `create-account` to create a **normal account**:
|
||||
|
||||
```
|
||||
./bin/create-account -config /path/to/dendrite.yaml -username USERNAME
|
||||
```
|
||||
|
||||
You will be prompted to enter a new password for the new account.
|
||||
|
||||
To create a new **admin account**, add the `-admin` flag:
|
||||
|
||||
```
|
||||
./bin/create-account -config /path/to/dendrite.yaml -username USERNAME -admin
|
||||
```
|
||||
|
||||
By default `create-account` uses `http://localhost:8008` to connect to Dendrite, this can be overwritten using the `-url` flag:
|
||||
|
||||
```
|
||||
./bin/create-account -config /path/to/dendrite.yaml -username USERNAME -url https://localhost:8448
|
||||
```
|
||||
|
||||
An example of using `create-account` when running in **Docker**, having found the `CONTAINERNAME` from `docker ps`:
|
||||
|
||||
```
|
||||
docker exec -it CONTAINERNAME /usr/bin/create-account -config /path/to/dendrite.yaml -username USERNAME
|
||||
```
|
||||
|
||||
```
|
||||
docker exec -it CONTAINERNAME /usr/bin/create-account -config /path/to/dendrite.yaml -username USERNAME -admin
|
||||
```
|
||||
|
||||
Dendrite supports the Synapse-compatible shared secret registration endpoint.
|
||||
|
||||
To enable shared secret registration, you must first enable it in the `dendrite.yaml` configuration file by specifying a shared secret. In the `client_api` section of the config, enter a new secret into the `registration_shared_secret` field:
|
||||
|
||||
```
|
||||
client_api:
|
||||
# ...
|
||||
registration_shared_secret: ""
|
||||
```
|
||||
|
||||
You can then use the `/_synapse/admin/v1/register` endpoint as per the [Synapse documentation](https://matrix-org.github.io/synapse/latest/admin_api/register_api.html).
|
||||
|
||||
Shared secret registration is only enabled once a secret is configured. To disable shared secret registration again, remove the secret from the configuration file.
|
||||
@@ -0,0 +1,239 @@
|
||||
---
|
||||
page-title: "How to Set Up a Mail Server with PostfixAdmin on Debian 11"
|
||||
url: https://www.howtoforge.com/how-to-set-up-a-mail-server-with-postfixadmin-on-debian-11/
|
||||
date: "2023-05-29 07:50:31"
|
||||
---
|
||||
### On this page
|
||||
|
||||
1. [Prerequisites](https://www.howtoforge.com/how-to-set-up-a-mail-server-with-postfixadmin-on-debian-11/#prerequisites)
|
||||
2. [Getting Started](https://www.howtoforge.com/how-to-set-up-a-mail-server-with-postfixadmin-on-debian-11/#getting-started)
|
||||
3. [Install Nginx, MariaDB and PHP](https://www.howtoforge.com/how-to-set-up-a-mail-server-with-postfixadmin-on-debian-11/#install-nginx-mariadb-and-php)
|
||||
4. [Create a PostfixAdmin Database](https://www.howtoforge.com/how-to-set-up-a-mail-server-with-postfixadmin-on-debian-11/#create-a-postfixadmin-database)
|
||||
5. [Install PostfixAdmin](https://www.howtoforge.com/how-to-set-up-a-mail-server-with-postfixadmin-on-debian-11/#install-postfixadmin)
|
||||
6. [Configure Nginx for PostfixAdmin](https://www.howtoforge.com/how-to-set-up-a-mail-server-with-postfixadmin-on-debian-11/#configure-nginx-for-postfixadmin)
|
||||
7. [Access PostfixAdmin](https://www.howtoforge.com/how-to-set-up-a-mail-server-with-postfixadmin-on-debian-11/#access-postfixadmin)
|
||||
8. [Conclusion](https://www.howtoforge.com/how-to-set-up-a-mail-server-with-postfixadmin-on-debian-11/#conclusion)
|
||||
|
||||
PostfixAdmin is a free, open-source, and web-based interface used for managing Postfix mail server from the web browser. It allows you to add users, aliases, set a disk quota, add and remove domains from the web-based interface. It supports several database backends including PostgreSQL, MySQL, MariaDB, and SQLite. It can be integrated with Squirrelmail and Roundcube via plugins.
|
||||
|
||||
In this article, I will explain how to install PostfixAdmin on Debian 11.
|
||||
|
||||
## Prerequisites
|
||||
|
||||
- A server running Debian 11 with postfix installed.
|
||||
- A valid domain name is pointed with your server IP address.
|
||||
- A valid MX record is pointed with your server IP address.
|
||||
|
||||
## Getting Started
|
||||
|
||||
First, update your system packages with the latest version using the following command:
|
||||
|
||||
apt-get update -y
|
||||
|
||||
Once your system is updated, set the fully qualified hostname of your server.
|
||||
|
||||
hostnamectl set-hostname mail.domain.com
|
||||
|
||||
Next, run the following command to apply the changes.
|
||||
|
||||
hostname -f
|
||||
|
||||
Once you are done, you can proceed to the next step.
|
||||
|
||||
## Install Nginx, MariaDB and PHP
|
||||
|
||||
Next, you will need to install the Nginx web server, MariaDB, PHP, and other required PHP extensions to your server. You can install all of them with the following command:
|
||||
|
||||
apt-get install nginx mariadb-server php-fpm php-cli php-imap php-json php-mysql php-opcache php-mbstring php-readline unzip sudo -y
|
||||
|
||||
Once all the packages are installed, you can proceed to the next step.
|
||||
|
||||
## Create a PostfixAdmin Database
|
||||
|
||||
Next, you will need to create a database and user for PostfixAdmin. First, log in to the MariaDB console with the following command:
|
||||
|
||||
mysql
|
||||
|
||||
Once you are connected, create a database and user with the following command:
|
||||
|
||||
MariaDB \[(none)\]> CREATE DATABASE postfixadmin;
|
||||
MariaDB \[(none)\]> GRANT ALL ON postfixadmin.\* TO 'postfixadmin'@'localhost' IDENTIFIED BY 'securepassword';
|
||||
|
||||
Next, flush the privileges and exit from the MariaDB shell with the following command:
|
||||
|
||||
MariaDB \[(none)\]> FLUSH PRIVILEGES;
|
||||
MariaDB \[(none)\]> EXIT;
|
||||
|
||||
At this point, the MariaDB database is created for PostfixAdmin. You can now proceed to the next step.
|
||||
|
||||
## Install PostfixAdmin
|
||||
|
||||
First, you will need to download the latest version of PostfixAdmin from the Sourceforge website. You can download it with the following command:
|
||||
|
||||
wget https://webwerks.dl.sourceforge.net/project/postfixadmin/postfixadmin-3.3.8/PostfixAdmin%203.3.8.tar.gz
|
||||
|
||||
Once the download is completed, extract the downloaded file with the following command:
|
||||
|
||||
tar -xvzf PostfixAdmin\\ 3.3.8.tar.gz
|
||||
|
||||
Next, move the extracted directory to the Nginx web root directory:
|
||||
|
||||
mv postfixadmin-postfixadmin-7d04685 /var/www/html/postfixadmin
|
||||
|
||||
Next, create a directory required to install PostfixAdmin:
|
||||
|
||||
mkdir /var/www/html/postfixadmin/templates\_c
|
||||
|
||||
Next, set proper ownership to PostfixAdmin directory:
|
||||
|
||||
chown -R www-data: /var/www/html/postfixadmin/
|
||||
|
||||
Next, create a config.local.php file:
|
||||
|
||||
nano /var/www/html/postfixadmin/config.local.php
|
||||
|
||||
Add the following lines:
|
||||
|
||||
<?php
|
||||
$CONF\['configured'\] = true;
|
||||
|
||||
$CONF\['database\_type'\] = 'mysqli';
|
||||
$CONF\['database\_host'\] = 'localhost';
|
||||
$CONF\['database\_user'\] = 'postfixadmin';
|
||||
$CONF\['database\_password'\] = 'securepassword';
|
||||
$CONF\['database\_name'\] = 'postfixadmin';
|
||||
|
||||
$CONF\['default\_aliases'\] = array (
|
||||
'abuse' => 'abuse@domain.com',
|
||||
'hostmaster' => 'hostmaster@domain.com',
|
||||
'postmaster' => 'postmaster@domain.com',
|
||||
'webmaster' => 'webmaster@domain.com'
|
||||
);
|
||||
|
||||
$CONF\['fetchmail'\] = 'NO';
|
||||
$CONF\['show\_footer\_text'\] = 'NO';
|
||||
|
||||
$CONF\['quota'\] = 'YES';
|
||||
$CONF\['domain\_quota'\] = 'YES';
|
||||
$CONF\['quota\_multiplier'\] = '1024000';
|
||||
$CONF\['used\_quotas'\] = 'YES';
|
||||
$CONF\['new\_quota\_table'\] = 'YES';
|
||||
|
||||
$CONF\['aliases'\] = '0';
|
||||
$CONF\['mailboxes'\] = '0';
|
||||
$CONF\['maxquota'\] = '0';
|
||||
$CONF\['domain\_quota\_default'\] = '0';
|
||||
?>
|
||||
|
||||
Save and close the file then create the schema for the PostfixAdmin database with the following command:
|
||||
|
||||
sudo -u www-data php /var/www/html/postfixadmin/public/upgrade.php
|
||||
|
||||
Next, you will need to create a super admin account for PostfixAdmin. You can create it with the following command:
|
||||
|
||||
bash /var/www/html/postfixadmin/scripts/postfixadmin-cli admin add
|
||||
|
||||
Provide your admin username, password, and domain as shown below:
|
||||
|
||||
Welcome to Postfixadmin-CLI v0.3
|
||||
---------------------------------------------------------------
|
||||
|
||||
Admin:
|
||||
> admin@domain.com
|
||||
|
||||
Password:
|
||||
> Secure@12345
|
||||
|
||||
Password (again):
|
||||
> Secure@12345
|
||||
|
||||
Super admin:
|
||||
(Super admins have access to all domains, can manage domains and admin accounts.) (y/n)
|
||||
> y
|
||||
|
||||
Domain:
|
||||
> domain.com
|
||||
|
||||
Active: (y/n)
|
||||
> y
|
||||
|
||||
The admin admin@domain.com has been added!
|
||||
|
||||
---------------------------------------------------------------
|
||||
|
||||
## Configure Nginx for PostfixAdmin
|
||||
|
||||
Next, you will need to create an Nginx virtual host configuration file for PostfixAdmin. You can create it with the following command:
|
||||
|
||||
nano /etc/nginx/conf.d/domain.com.conf
|
||||
|
||||
Add the following lines:
|
||||
|
||||
server {
|
||||
listen 80;
|
||||
root /var/www/html/postfixadmin/public;
|
||||
index index.html index.htm index.php;
|
||||
server\_name mail.domain.com;
|
||||
|
||||
location ~ \\.php$ {
|
||||
fastcgi\_split\_path\_info ^(.+\\.php)(/.+)$;
|
||||
fastcgi\_pass unix:/var/run/php/php7.4-fpm.sock;
|
||||
fastcgi\_index index.php;
|
||||
include fastcgi\_params;
|
||||
fastcgi\_param SCRIPT\_FILENAME $document\_root$fastcgi\_script\_name;
|
||||
fastcgi\_intercept\_errors off;
|
||||
fastcgi\_buffer\_size 16k;
|
||||
fastcgi\_buffers 4 16k;
|
||||
fastcgi\_connect\_timeout 600;
|
||||
fastcgi\_send\_timeout 600;
|
||||
fastcgi\_read\_timeout 600;
|
||||
}
|
||||
|
||||
|
||||
location / {
|
||||
try\_files $uri $uri/ =404;
|
||||
}
|
||||
|
||||
}
|
||||
|
||||
Save and close the file then restart the Nginx service to apply the changes:
|
||||
|
||||
systemctl restart nginx
|
||||
|
||||
You can also check the status of Nginx with the following command:
|
||||
|
||||
systemctl status nginx
|
||||
|
||||
You should get the following output:
|
||||
|
||||
? nginx.service - A high performance web server and a reverse proxy server
|
||||
Loaded: loaded (/lib/systemd/system/nginx.service; enabled; vendor preset: enabled)
|
||||
Active: active (running) since Sat 2021-08-28 08:13:22 UTC; 7s ago
|
||||
Docs: man:nginx(8)
|
||||
Process: 74644 ExecStartPre=/usr/sbin/nginx -t -q -g daemon on; master\_process on; (code=exited, status=0/SUCCESS)
|
||||
Process: 74645 ExecStart=/usr/sbin/nginx -g daemon on; master\_process on; (code=exited, status=0/SUCCESS)
|
||||
Main PID: 74646 (nginx)
|
||||
Tasks: 2 (limit: 2341)
|
||||
Memory: 3.2M
|
||||
CPU: 57ms
|
||||
CGroup: /system.slice/nginx.service
|
||||
??74646 nginx: master process /usr/sbin/nginx -g daemon on; master\_process on;
|
||||
??74647 nginx: worker process
|
||||
|
||||
Aug 28 08:13:22 mail.domain.com systemd\[1\]: Starting A high performance web server and a reverse proxy server...
|
||||
Aug 28 08:13:22 mail.domain.com systemd\[1\]: nginx.service: Failed to parse PID from file /run/nginx.pid: Invalid argument
|
||||
Aug 28 08:13:22 mail.domain.com systemd\[1\]: Started A high performance web server and a reverse proxy server.
|
||||
|
||||
## Access PostfixAdmin
|
||||
|
||||
At this point, PostfixAdmin is installed and configured. You can now access it using the URL **http://mail.domain.com**. You will be redirected to the PostfixAdmin login page:
|
||||
|
||||
[](https://www.howtoforge.com/images/how_to_set_up_a_mail_server_with_postfixadmin_on_debian_11/big/p1.png)
|
||||
|
||||
Provide your admin email, password and click on the **Login** button. You should see the PostfixAdmin dashboard on the following screen:
|
||||
|
||||
[](https://www.howtoforge.com/images/how_to_set_up_a_mail_server_with_postfixadmin_on_debian_11/big/p2.png)
|
||||
|
||||
## Conclusion
|
||||
|
||||
Congratulations! you have successfully installed PostfixAdmin on Debian 11. You can now easily manage your Postfix mail server from the web browser. Feel free to ask me if you have any questions.
|
||||
@@ -0,0 +1,106 @@
|
||||
---
|
||||
page-title: "N26开户教程 | Mutou"
|
||||
url: https://www.mutou.men/posts/n26%E5%BC%80%E6%88%B7%E6%95%99%E7%A8%8B/
|
||||
date: "2023-05-30 17:45:21"
|
||||
---
|
||||
## 一、下载N26 app
|
||||
|
||||
去appstore或者google play搜索下载即可。网页注册需要挂德国代理,如果你有德国代理,点此连接在网页注册👉[注册地址](https://n26.com/r/haihuaw4351)
|
||||
|
||||
|
||||
|
||||
上面选择完成后,直接提交就可以。如果有reffer code填写的地方,可以填写haihuaw4351,各得15欧元。
|
||||
|
||||
注册完成后,下一步是视频验证。
|
||||
|
||||
## 二、视频验证
|
||||
|
||||
我是晚上8点左右验证的,接通比较快。 基本会有以下问题:
|
||||
|
||||
## 1.开户确认
|
||||
|
||||
询问你德语还是英语沟通
|
||||
|
||||
答:English
|
||||
|
||||
> 如果无法支持英文,直接挂掉,重新开启视频换人即可,遇到态度不好的同理。
|
||||
|
||||
1.1 请告诉我你的姓名
|
||||
|
||||
答:可以直接读拼音或字母
|
||||
|
||||
2.2 你的邮箱地址
|
||||
|
||||
答: . 读dot
|
||||
|
||||
2.3 你的邮箱是不是你自己一个人使用?
|
||||
|
||||
答:yes
|
||||
|
||||
2.4 密码是不是只有你一个人知道?
|
||||
|
||||
答:yes
|
||||
|
||||
2.5 开户的原因 (reason of open this account)
|
||||
|
||||
答:Shopping Online 等等
|
||||
|
||||
2.6 有沒有可以收验证码的手机 (Do you have any device for receive text message)
|
||||
|
||||
答:yes
|
||||
|
||||
2.7 从哪知道N26的(How to know N26)
|
||||
|
||||
答:my friend或者其他的
|
||||
|
||||
2.8 你的国籍 (National)
|
||||
|
||||
答:China
|
||||
|
||||
## 2 验证护照
|
||||
|
||||
1.给人脸拍照
|
||||
|
||||
细节:可能要求你手先在脸前挥动一下,然后张开5指放在脸旁**慢慢的**从左移动到右边 手速不要太快
|
||||
|
||||
2.给护照拍照
|
||||
|
||||
需要做如下指令:
|
||||
|
||||
2.1 翻到照片页,拍一个完整图片,调整角度,查看防伪水印。
|
||||
|
||||
2.2 将摄像头靠近护照头像拍照,有可能要手指按住头像拍照.
|
||||
|
||||
2.3 将摄像头靠近护照号码拍照
|
||||
|
||||
2.4 将摄像头靠近护照标拍照,注意:可能会要求你不断摆动角度,看颜色变化,会要求右手拇指或食指按住护照标一半的位置进行拍照.
|
||||
|
||||
2.5 将摄像头靠近护照水印拍照,要求**翻转不同角度看颜色变化**.
|
||||
|
||||
2.6 合上护照,给护照封面拍照。
|
||||
|
||||
顺序不一定,也不一定全做,也可能有其他要求。
|
||||
|
||||
## 3.合上护照回答个人信息
|
||||
|
||||
3.1 你的出生日期?
|
||||
|
||||
3.2 出生城市or国家?
|
||||
|
||||
3.3 你的护照号码? 用英语如是回答即可
|
||||
|
||||
3.4 你是否处于自己的意愿开户?
|
||||
|
||||
答:yes
|
||||
|
||||
3.5 你是否受别人指使开户?
|
||||
|
||||
答:no
|
||||
|
||||
3.6 开设账户只有你自己使用吗?
|
||||
|
||||
答:yes
|
||||
|
||||
## 4\. 填写短信验证码
|
||||
|
||||
会发送一个手机验证码,填完之后,客服会说视频认证完成了
|
||||
@@ -0,0 +1,244 @@
|
||||
---
|
||||
page-title: "PostfixAmavisNew - Community Help Wiki"
|
||||
url: https://help.ubuntu.com/community/PostfixAmavisNew
|
||||
date: "2023-05-25 09:42:29"
|
||||
---
|
||||
## Introduction
|
||||
|
||||
Contents
|
||||
|
||||
1. [Introduction](https://help.ubuntu.com/community/PostfixAmavisNew#Introduction)
|
||||
2. [Prerequisite](https://help.ubuntu.com/community/PostfixAmavisNew#Prerequisite)
|
||||
3. [Installation](https://help.ubuntu.com/community/PostfixAmavisNew#Installation)
|
||||
4. [Configuration](https://help.ubuntu.com/community/PostfixAmavisNew#Configuration)
|
||||
1. [Clamav](https://help.ubuntu.com/community/PostfixAmavisNew#Clamav)
|
||||
2. [Spamassassin](https://help.ubuntu.com/community/PostfixAmavisNew#Spamassassin)
|
||||
3. [Amavis](https://help.ubuntu.com/community/PostfixAmavisNew#Amavis)
|
||||
4. [Postfix integration](https://help.ubuntu.com/community/PostfixAmavisNew#Postfix_integration)
|
||||
5. [Test](https://help.ubuntu.com/community/PostfixAmavisNew#Test)
|
||||
6. [Troubleshooting](https://help.ubuntu.com/community/PostfixAmavisNew#Troubleshooting)
|
||||
7. [Amavis Performance](https://help.ubuntu.com/community/PostfixAmavisNew#Amavis_Performance)
|
||||
|
||||
In this howto, Postfix integration with amavis-new will be presented. Amavis-new is a wrapper that can call any number of content filtering programs for spam detection, antivirus, etc. In this howto, integration with Spamassassin and Clamav will be presented. This is a classical installation of Postfix + Amavis-new + Spamassassin + Clamav.
|
||||
|
||||
## Prerequisite
|
||||
|
||||
You should have a functional Postfix server installed. If this is not the case, follow the [Postfix](https://help.ubuntu.com/community/Postfix) guide.
|
||||
|
||||
## Installation
|
||||
|
||||
To begin, install (see [InstallingSoftware](https://help.ubuntu.com/community/InstallingSoftware)) the following packages:
|
||||
|
||||
sudo apt-get install amavisd-new spamassassin clamav-daemon
|
||||
|
||||
Install the optional packages for better spam detection (who does not want better spam detection?):
|
||||
|
||||
sudo apt-get install libnet-dns-perl libmail-spf-perl pyzor razor
|
||||
|
||||
Install these optional packages to enable better scanning of attached archive files:
|
||||
|
||||
sudo apt-get install arj bzip2 cabextract cpio file gzip lha nomarch pax rar unrar unzip unzoo zip zoo
|
||||
|
||||
**Note:** Ubuntu 12.04 LTS doesn't have unzoo. Ubuntu 14.04 LTS doesn't have lha. You may try to substitute lhasa.
|
||||
|
||||
## Configuration
|
||||
|
||||
## Clamav
|
||||
|
||||
The default behaviour of Clamav will fit our needs. A daemon is launched (clamd) and signatures are fetched every day. For more Clamav configuration options, check the configuration files in /etc/clamav.
|
||||
|
||||
Add clamav user to the amavis group and vice versa in order for Clamav to have access to scan files:
|
||||
|
||||
sudo adduser clamav amavis
|
||||
sudo adduser amavis clamav
|
||||
|
||||
**Note**: especially when driven on small cloud instances, VPS or routers there were concerns about the memory consumption. There is a good summary why virus scanning in general has a [rather high memory](http://unix.stackexchange.com/questions/114709/how-to-reduce-clamav-memory-usage) consumption in general. An admin setting up such a solution needs to consider that ~200-350mb seem to be rather normal.
|
||||
|
||||
## Spamassassin
|
||||
|
||||
As amavis is its own spamassassin-daemon (amavis uses the spamassassin libraries), there is no need in configuring or starting spamassassin. amavis will not use any running instance of spamd!
|
||||
|
||||
The use of razor and pyzormust be enabled by
|
||||
|
||||
\# su - amavis -s /bin/bash
|
||||
\# razor-admin -create
|
||||
\# razor-admin -register
|
||||
\# pyzor discover
|
||||
|
||||
There is no need of configuring razor or pyzor.
|
||||
|
||||
## Amavis
|
||||
|
||||
First, activate spam and antivirus detection in Amavis by editing /etc/amavis/conf.d/15-content\_filter\_mode:
|
||||
|
||||
use strict;
|
||||
\# You can modify this file to re-enable SPAM checking through spamassassin
|
||||
\# and to re-enable antivirus checking.
|
||||
#
|
||||
\# Default antivirus checking mode
|
||||
\# Uncomment the two lines below to enable it
|
||||
#
|
||||
@bypass\_virus\_checks\_maps = (
|
||||
\\%bypass\_virus\_checks, \\@bypass\_virus\_checks\_acl, \\$bypass\_virus\_checks\_re);
|
||||
#
|
||||
\# Default SPAM checking mode
|
||||
\# Uncomment the two lines below to enable it
|
||||
#
|
||||
@bypass\_spam\_checks\_maps = (
|
||||
\\%bypass\_spam\_checks, \\@bypass\_spam\_checks\_acl, \\$bypass\_spam\_checks\_re);
|
||||
1; # insure a defined return
|
||||
|
||||
After configuration Amavis needs to be restarted:
|
||||
|
||||
sudo /etc/init.d/amavis restart
|
||||
|
||||
## Postfix integration
|
||||
|
||||
For postfix integration, you need to add the content\_filter configuration variable to the Postfix configuration file /etc/postfix/main.cf. This instructs postfix to pass messages to amavis at a given IP address and port:
|
||||
|
||||
content\_filter = smtp-amavis:\[127.0.0.1\]:10024
|
||||
|
||||
The following postconf command, run as root because of the preceding sudo command, adds the content\_filter specification line above to main.cf:
|
||||
|
||||
sudo postconf -e "content\_filter = smtp-amavis:\[127.0.0.1\]:10024"
|
||||
|
||||
Alternatively, you can manually edit main.cf yourself to add the content\_filter line.
|
||||
|
||||
Next edit /etc/postfix/master.cf and add the following to the end of the file:
|
||||
|
||||
smtp-amavis unix - - - - 2 smtp
|
||||
-o smtp\_data\_done\_timeout=1200
|
||||
-o smtp\_send\_xforward\_command=yes
|
||||
-o disable\_dns\_lookups=yes
|
||||
-o max\_use=20
|
||||
127.0.0.1:10025 inet n - - - - smtpd
|
||||
-o content\_filter=
|
||||
-o local\_recipient\_maps=
|
||||
-o relay\_recipient\_maps=
|
||||
-o smtpd\_restriction\_classes=
|
||||
-o smtpd\_delay\_reject=no
|
||||
-o smtpd\_client\_restrictions=permit\_mynetworks,reject
|
||||
-o smtpd\_helo\_restrictions=
|
||||
-o smtpd\_sender\_restrictions=
|
||||
-o smtpd\_recipient\_restrictions=permit\_mynetworks,reject
|
||||
-o smtpd\_data\_restrictions=reject\_unauth\_pipelining
|
||||
-o smtpd\_end\_of\_data\_restrictions=
|
||||
-o mynetworks=127.0.0.0/8
|
||||
-o smtpd\_error\_sleep\_time=0
|
||||
-o smtpd\_soft\_error\_limit=1001
|
||||
-o smtpd\_hard\_error\_limit=1000
|
||||
-o smtpd\_client\_connection\_count\_limit=0
|
||||
-o smtpd\_client\_connection\_rate\_limit=0
|
||||
-o receive\_override\_options=no\_header\_body\_checks,no\_unknown\_recipient\_checks
|
||||
|
||||
Also add the following two lines immediately below the "pickup" transport service:
|
||||
|
||||
-o content\_filter=
|
||||
-o receive\_override\_options=no\_header\_body\_checks
|
||||
|
||||
This will prevent messages that are generated to report on spam from being classified as spam.
|
||||
|
||||
For Postfix instances hosting virtual domains, Amavis also need to know what domain names are considered as local domain names. By default, only the FQDN of the localhost is treated as local. So in the file '/etc/amavis/conf.d/05-domain\_id', list all your virtual domain names in @local\_domains\_acl
|
||||
|
||||
@local\_domains\_acl = ( ".$mydomain", ".example1.com", ".example2.com" );
|
||||
|
||||
And In the file '/etc/amavis/conf.d/50-user', add
|
||||
|
||||
@whitelist\_sender\_acl = @local\_domains\_acl
|
||||
|
||||
More information can be found from ["README.postfix from amavisd-new"](http://www.ijs.si/software/amavisd/README.postfix.txt) and ["D.J.Fan"](http://www200.pair.com/mecham/spam/spamfilter20060701.html)
|
||||
|
||||
Reload postfix:
|
||||
|
||||
sudo /etc/init.d/postfix reload
|
||||
|
||||
Now content filtering with spam and virus detection is enabled.
|
||||
|
||||
## Test
|
||||
|
||||
First, test that the amavis SMTP is listening:
|
||||
|
||||
telnet localhost 10024
|
||||
Trying 127.0.0.1...
|
||||
Connected to localhost.
|
||||
Escape character is '^\]'.
|
||||
220 \[127.0.0.1\] ESMTP amavisd-new service ready
|
||||
^\]
|
||||
|
||||
Check on your /var/log/mail.log that everything goes well. If you raise the log level, you can check every step of the content filtering: spam check, virus check, etc. Don't forget to lower the log level after your checks!
|
||||
|
||||
On messages that go through the content filter you should see:
|
||||
|
||||
X-Spam-Level:
|
||||
X-Virus-Scanned: Debian amavisd-new at example.com
|
||||
X-Spam-Status: No, hits=-2.3 tagged\_above=-1000.0 required=5.0 tests=AWL, BAYES\_00
|
||||
X-Spam-Level:
|
||||
|
||||
**Note:** $sa\_tag\_level in /etc/amavis/conf.d/20-debian\_defaults must be lower than spam hit rating for the header to appear on the message. For troubleshooting set $sa\_tag\_level to -999
|
||||
|
||||
## Troubleshooting
|
||||
|
||||
If the filtering is not happening, adding the following to /etc/amavis/conf.d/50-user may help:
|
||||
|
||||
@local\_domains\_acl = ( ".$mydomain" );
|
||||
|
||||
If you receive mail for other domains, add them to the list. This information was obtained from the Amavis-New FAQ [here](http://www.ijs.si/software/amavisd/#faq-spam).
|
||||
|
||||
If you see the following error in /var/log/syslog when amavisd is trying to scan a message:
|
||||
|
||||
amavis\[30807\]: (30807-01) (!!) ask\_av (ClamAV-clamd) FAILED - unexpected result: /var/lib/amavis/tmp/amavis-20070615T125025-30807/parts: lstat() failed. ERROR\\n
|
||||
|
||||
Try changing the permissions on /var/lib/amavis/tmp:
|
||||
|
||||
chmod -R 775 /var/lib/amavis/tmp
|
||||
|
||||
You can also change AllowSupplementaryGroups in /etc/clamav/clamd.conf:
|
||||
|
||||
AllowSupplementaryGroups true
|
||||
|
||||
Another way to trouble shoot errors associated with Amavisd-new, Spamassassin, Postfix, or Clamav is to restart all the services with Amavisd-new being the last one to start:
|
||||
|
||||
sudo /etc/init.d/postfix restart
|
||||
sudo /etc/init.d/spamassassin restart
|
||||
sudo /etc/init.d/clamav-daemon restart
|
||||
sudo /etc/init.d/amavis restart
|
||||
|
||||
Then check /var/log/mail.log and see if the error has gone away.
|
||||
|
||||
**Note**: $sa\_tag\_level in /etc/amavis/conf.d/20-debian\_defaults must be lower than spam hit rating for the header to appear on the message. For troubleshooting set $sa\_tag\_level to -999
|
||||
|
||||
## Amavis Performance
|
||||
|
||||
To increase the number of processes that amavisd-new uses above the default 2 edit the file /etc/amavis/conf.d/50-user inserting the line:
|
||||
|
||||
$max\_servers = X;
|
||||
|
||||
above the line:
|
||||
|
||||
#------------ Do not modify anything below this line -------------
|
||||
|
||||
where X is the number of processes you wish amavis to use.
|
||||
|
||||
Amend the following line in /etc/postfix/master.cf with the same value for the max\_procs (marked below as X)
|
||||
|
||||
smtp-amavis unix - - - - X smtp
|
||||
|
||||
Restart amavis and reload postfix's config
|
||||
|
||||
sudo /etc/init.d/amavis restart
|
||||
sudo postfix reload
|
||||
|
||||
You can check the configuration change has taken affect by running amavisd-nanny:
|
||||
|
||||
sudo amavisd-nanny
|
||||
|
||||
For guidance on how many processes to set this value to please see:
|
||||
|
||||
zcat /usr/share/doc/amavisd-new/README.performance.gz | less
|
||||
|
||||
and [http://www.ijs.si/software/amavisd/amavisd-new-magdeburg-20050519.pdf](http://www.ijs.si/software/amavisd/amavisd-new-magdeburg-20050519.pdf)
|
||||
|
||||
|
||||
**Note:** This guide has been tested on Ubuntu 7.10 (Gutsy Gibbon), Ubuntu 10.04 LTS Server (Lucid Lynx), Ubuntu 12.04.3 LTS (Precise Pangolin), Ubuntu 14.04.2 LTS (Trusty Tahr), and Ubuntu 20.04 LTS (Focal Fossa).
|
||||
|
||||
---
|
||||
+529
@@ -0,0 +1,529 @@
|
||||
---
|
||||
page-title: "Setting Up Amavis and ClamAV on Ubuntu Mail Server - LinuxBabe"
|
||||
url: https://www.linuxbabe.com/mail-server/postfix-amavis-spamassassin-clamav-ubuntu
|
||||
date: "2023-05-25 10:56:40"
|
||||
---
|
||||
This is part 11 in the Ubuntu mail server from scratch tutorial series. In this article, I will show you how to use **Amavis** and **ClamAV** to scan viruses in email messages.
|
||||
|
||||
**Amavis** (A Mail Virus Scanner) is a high-performance interface between a message transfer agent (MTA) such as **Postfix** and content filters. A content filter is a program that scans the headers and body of an email message, and usually takes some action based on what it finds. The most common examples are **ClamAV virus scanner** and **SpamAssassin**.
|
||||
|
||||
|
||||
|
||||
Amavis speaks standard SMTP protocol and can also use the Sendmail milter interface. It’s commonly used for
|
||||
|
||||
- virus-scanning by integrating with ClamAV (Clam AntiVirus)
|
||||
- spam-checking by integrating with SpamAssassin
|
||||
- DKIM signing and verification. (Actually, I prefer to use OpenDKIM for DKIM signing and verification.)
|
||||
|
||||
## Prerequisites
|
||||
|
||||
You should have completed at least [part 1 (Postfix SMTP server)](https://www.linuxbabe.com/mail-server/setup-basic-postfix-mail-sever-ubuntu) and [part 2 (Dovecot IMAP server)](https://www.linuxbabe.com/mail-server/secure-email-server-ubuntu-postfix-dovecot) of the Ubuntu mail server from scratch tutorial series. Note that if you used [iRedMail](https://www.linuxbabe.com/mail-server/ubuntu-20-04-iredmail-server-installation) or [Modoboa](https://www.linuxbabe.com/mail-server/email-server-ubuntu-18-04-modoboa) to set up your mail server, then Amavis and ClamAV are already installed and configured, so you don’t need to follow this tutorial.
|
||||
|
||||
**Warning**: Amavis and ClamAV require a fair amount of RAM. Make sure you have at least 1.3 GB free RAM on your server before installing Amavis and ClamAV. The whole mail server stack (Postfix, Dovecot, Amavis, ClamAV, SpamAssassin, OpenDKIM, MySQL/MariaDB, PostfixAdmin, and Roundcube Webmail) needs at least **3 GB** RAM to run smoothly. If your RAM runs out, you are going to have troubles like mail server going offline or unresponsive.
|
||||
|
||||
## Step 1: Install Amavis on Ubuntu
|
||||
|
||||
Amvis is available from the default Ubuntu repository, so run the following command to install it.
|
||||
|
||||
sudo apt install amavisd-new -y
|
||||
|
||||
Once installed, it automatically starts. You can check its status with:
|
||||
|
||||
systemctl status amavis
|
||||
|
||||
Output:
|
||||
|
||||
● amavis.service - LSB: Starts amavisd-new mailfilter
|
||||
Loaded: loaded (/etc/init.d/amavis; generated)
|
||||
Active: **active (running)** since Fri 2020-08-07 15:43:40 HKT; 1min 1s ago
|
||||
Docs: man:systemd-sysv-generator(8)
|
||||
Tasks: 3 (limit: 9451)
|
||||
Memory: 75.4M
|
||||
CGroup: /system.slice/amavis.service
|
||||
├─1794260 /usr/sbin/amavisd-new (master)
|
||||
├─1794263 /usr/sbin/amavisd-new (virgin child)
|
||||
└─1794264 /usr/sbin/amavisd-new (virgin child)
|
||||
|
||||
If it’s not running, you can start it with:
|
||||
|
||||
sudo systemctl start amavis
|
||||
|
||||
Enable auto-start at boot time.
|
||||
|
||||
sudo systemctl enable amavis
|
||||
|
||||
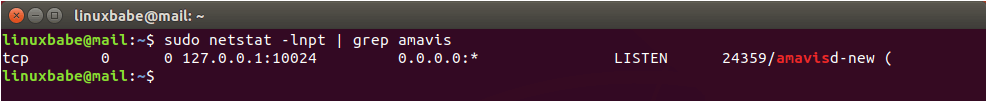
By default, it listen on *127.0.0.1:10024*, as can be seen with:
|
||||
|
||||
sudo netstat -lnpt | grep amavis
|
||||
|
||||
|
||||
|
||||
And it runs as the `amavis` user. To check the version number, run
|
||||
|
||||
amavisd-new -V
|
||||
|
||||
Sample output:
|
||||
|
||||
amavisd-new-2.11.0 (20160426)
|
||||
|
||||
To check the logs of Amavis, you can run
|
||||
|
||||
sudo journalctl -eu amavis
|
||||
|
||||
Viruses are commonly spread as attachments to email messages. Install the following packages for Amavis to extract and scan archive files in email messages such as `.7z`, `.cab`, `.doc`, `.exe`, `.iso`, `.jar`, and `.rar` files.
|
||||
|
||||
sudo apt install arj bzip2 cabextract cpio rpm2cpio file gzip lhasa nomarch pax rar unrar p7zip-full unzip zip lrzip lzip liblz4-tool lzop unrar-free
|
||||
|
||||
If you use Ubuntu 18.04, then also install the `ripole` package.
|
||||
|
||||
sudo apt install ripole
|
||||
|
||||
Note that if your server doesn’t use a fully-qualified domain name (FQDN) as the hostname, Amavis might fail to start. And the OS hostname might change, so it’s recommended to set a valid hostname directly in the Amavis configuration file.
|
||||
|
||||
sudo nano /etc/amavis/conf.d/05-node\_id
|
||||
|
||||
Find the following line.
|
||||
|
||||
#$myhostname = "mail.example.com";
|
||||
|
||||
Remove the comment character (#) and change `mail.example.com` to your real hostname.
|
||||
|
||||
$myhostname = "mail.linuxbabe.com";
|
||||
|
||||
Save and close the file. Restart Amavis for the changes to take effect.
|
||||
|
||||
sudo systemctl restart amavis
|
||||
|
||||
## Step 2: Integrate Postfix SMTP Server With Amavis
|
||||
|
||||
Amavisd-new works as an SMTP proxy. Email is fed to it through SMTP, processed, and fed back to the MTA through a new SMTP connection.
|
||||
|
||||
Edit the Postfix main configuration file.
|
||||
|
||||
sudo nano /etc/postfix/main.cf
|
||||
|
||||
Add the following line at the end of the file. This tells Postfix to turn on content filtering by sending every incoming email message to Amavis, which listens on *127.0.0.1:10024*.
|
||||
|
||||
content\_filter = smtp-amavis:\[127.0.0.1\]:10024
|
||||
|
||||
Also, add the following line.
|
||||
|
||||
smtpd\_proxy\_options = speed\_adjust
|
||||
|
||||
This will delay Postfix connection to content filter until the entire email message has been received, which can prevent content filters from wasting time and resources for slow SMTP clients.
|
||||
|
||||
Save and close the file. Then edit the `master.cf` file.
|
||||
|
||||
sudo nano /etc/postfix/master.cf
|
||||
|
||||
Add the following lines at the end of the file. This instructs Postfix to use a special SMTP client component called `smtp-amavis` to deliver email messages to Amavis. Please allow at least one whitespace character (tab or spacebar) before each `-o`. In postfix configurations, a preceding whitespace character means that this line is continuation of the previous line.
|
||||
|
||||
smtp-amavis unix - - n - 2 smtp
|
||||
-o syslog\_name=postfix/amavis
|
||||
-o smtp\_data\_done\_timeout=1200
|
||||
-o smtp\_send\_xforward\_command=yes
|
||||
-o disable\_dns\_lookups=yes
|
||||
-o max\_use=20
|
||||
-o smtp\_tls\_security\_level=none
|
||||
|
||||
Then add the following lines at the end of the file. This tells Postfix to run an additional smtpd daemon listening on *127.0.0.1:10025* to receive email messages back from Amavis.
|
||||
|
||||
127.0.0.1:10025 inet n - n - - smtpd
|
||||
-o syslog\_name=postfix/10025
|
||||
-o content\_filter=
|
||||
-o mynetworks\_style=host
|
||||
-o mynetworks=127.0.0.0/8
|
||||
-o local\_recipient\_maps=
|
||||
-o relay\_recipient\_maps=
|
||||
-o strict\_rfc821\_envelopes=yes
|
||||
-o smtp\_tls\_security\_level=none
|
||||
-o smtpd\_tls\_security\_level=none
|
||||
-o smtpd\_restriction\_classes=
|
||||
-o smtpd\_delay\_reject=no
|
||||
-o smtpd\_client\_restrictions=permit\_mynetworks,reject
|
||||
-o smtpd\_helo\_restrictions=
|
||||
-o smtpd\_sender\_restrictions=
|
||||
-o smtpd\_recipient\_restrictions=permit\_mynetworks,reject
|
||||
-o smtpd\_end\_of\_data\_restrictions=
|
||||
-o smtpd\_error\_sleep\_time=0
|
||||
-o smtpd\_soft\_error\_limit=1001
|
||||
-o smtpd\_hard\_error\_limit=1000
|
||||
-o smtpd\_client\_connection\_count\_limit=0
|
||||
-o smtpd\_client\_connection\_rate\_limit=0
|
||||
-o receive\_override\_options=no\_header\_body\_checks,no\_unknown\_recipient\_checks,no\_address\_mappings
|
||||
|
||||
Save and close the file. Restart Postfix for the changes to take effect.
|
||||
|
||||
sudo systemctl restart postfix
|
||||
|
||||
## Step 3: Integrate Amavis with ClamAV
|
||||
|
||||
Now that Postfix can pass incoming emails to Amavis, we need to install the ClamAV virus scanner and integrate it with Amavis, so incoming emails can be scanned by ClamAV.
|
||||
|
||||
Install ClamAV on Ubuntu.
|
||||
|
||||
sudo apt install clamav clamav-daemon
|
||||
|
||||
There will be two systemd services installed by ClamAV:
|
||||
|
||||
- `clamav-daemon.service`: the Clam AntiVirus userspace daemon
|
||||
- `clamav-freshclam.service`: the ClamAV virus database updater
|
||||
|
||||
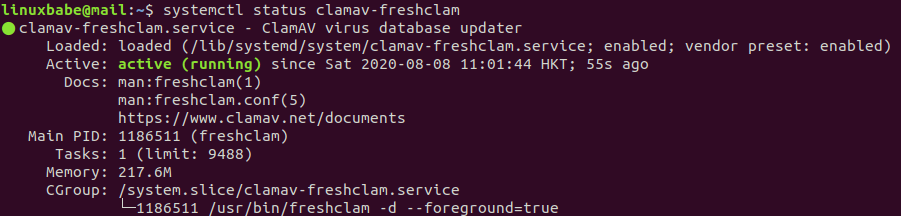
First, check the status of `clamav-freshclam.service`.
|
||||
|
||||
systemctl status clamav-freshclam
|
||||
|
||||
|
||||
|
||||
As you can see, it’s active (running) and uses 217.6M RAM on my mail server. Then check the journal/log.
|
||||
|
||||
sudo journalctl -eu clamav-freshclam
|
||||
|
||||
Output:
|
||||
|
||||

|
||||
|
||||
Hint: If the above command doesn’t quit immediately, press the Q key to make it quit.
|
||||
|
||||
We can see that `freshclam` downloaded 3 virus databases. CVD stands for ClamAV Virus Database.
|
||||
|
||||
- daily.cvd
|
||||
- main.cvd
|
||||
- bytecode.cvd
|
||||
|
||||
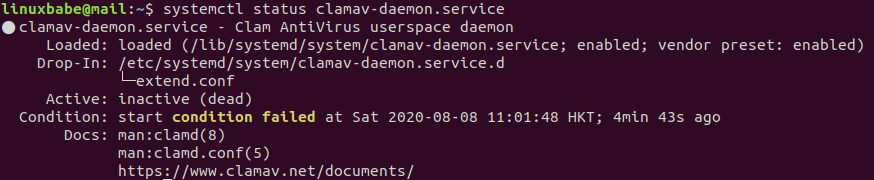
However, `clamd` was not notified because freshclam can’t connect to clamd through `/var/run/clamav/clamd.ctl`. Check the status of `clamav-daemon.service`.
|
||||
|
||||
systemctl status clamav-daemon
|
||||
|
||||
Output:
|
||||
|
||||
|
||||
|
||||
As you can see, it failed to start because a condition wasn’t met. In the `/lib/systemd/system/clamav-daemon.service` file, there are two conditions:
|
||||
|
||||
ConditionPathExistsGlob=/var/lib/clamav/main.{c\[vl\]d,inc}
|
||||
ConditionPathExistsGlob=/var/lib/clamav/daily.{c\[vl\]d,inc}
|
||||
|
||||
The `clamav-daemon.service` failed to start because main.cvd and daily.cvd were not downloaded yet when it starts. So we just need to restart this service.
|
||||
|
||||
sudo systemctl restart clamav-daemon
|
||||
|
||||
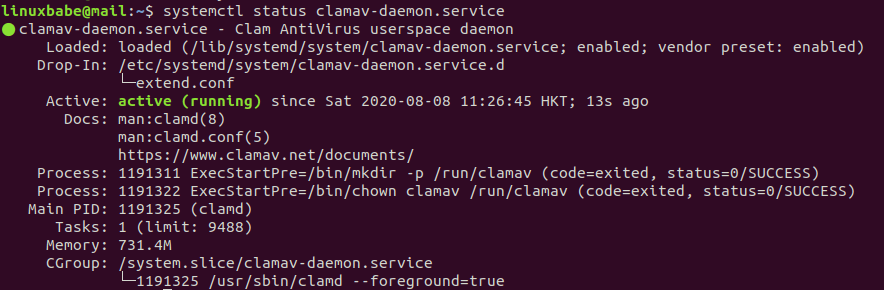
Now it should be running. By the way, it uses 731.4M RAM on my mail server. If your mail server doesn’t have enough RAM left, the service will fail.
|
||||
|
||||
systemctl status clamav-daemon.service
|
||||
|
||||
|
||||
|
||||
The `clamav-freshclam.service` will check ClamAV virus database updates once per hour.
|
||||
|
||||
Now we need to turn on virus-checking in Amavis.
|
||||
|
||||
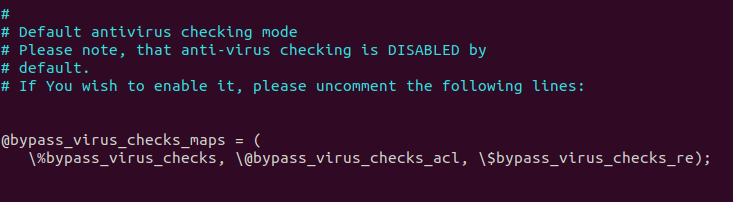
sudo nano /etc/amavis/conf.d/15-content\_filter\_mode
|
||||
|
||||
Uncomment the following lines to enable virus-checking.
|
||||
|
||||
#@bypass\_virus\_checks\_maps = (
|
||||
# \\%bypass\_virus\_checks, \\@bypass\_virus\_checks\_acl, \\$bypass\_virus\_checks\_re);
|
||||
|
||||
|
||||
|
||||
Save and close the file. There are lots of antivirus scanners in the `/etc/amavis/conf.d/15-av_scanners` file. ClamAV is the default. Amavis will call ClamAV via the `/var/run/clamav/clamd.ctl` Unix socket. We need to add user `clamav` to the `amavis` group.
|
||||
|
||||
sudo adduser clamav amavis
|
||||
|
||||
Then restart Amavis and ClamAV daemon for the changes to take effect.
|
||||
|
||||
sudo systemctl restart amavis clamav-daemon
|
||||
|
||||
Check the logs.
|
||||
|
||||
sudo journalctl -eu amavis
|
||||
|
||||
You can see that Amavis is now using ClamAV to scan viruses.
|
||||
|
||||
Aug 08 17:26:19 mail.linuxbabe.com amavis\[1233432\]: Using primary internal av scanner code for ClamAV-clamd
|
||||
Aug 08 17:26:19 mail.linuxbabe.com amavis\[1233432\]: Found secondary av scanner ClamAV-clamscan at /usr/bin/clamscan
|
||||
|
||||
Now if you send an email from other mail servers like Gmail to your own mail server and check the email headers, you can find a line like below, which indicates this email has been scanned by Amavis.
|
||||
|
||||
X-Virus-Scanned: Debian amavisd-new at linuxbabe.com
|
||||
|
||||
You should also check the mail log (`/var/log/mail.log`) to find if there are any errors.
|
||||
|
||||
## Step 4: Use A Dedicated Port for Email Submissions
|
||||
|
||||
ClamAV can scan both incoming and outgoing emails now. Amavis listens on port 10024 for both incoming and outgoing email messages. However, it’s a good practice to use a different port such as 10026 for email submissions from authenticated users. Edit the Amavis configuration file.
|
||||
|
||||
sudo nano /etc/amavis/conf.d/50-user
|
||||
|
||||
Custom settings should be added between the `use strict;` and `1;` line. By default, Amavis only listens on port 10024. Add the following line to make it also listen on port 10026.
|
||||
|
||||
$inet\_socket\_port = \[10024,10026\];
|
||||
|
||||
Then add the following line, which sets the “ORIGINATING” policy for port 10026.
|
||||
|
||||
$interface\_policy{'10026'} = 'ORIGINATING';
|
||||
|
||||
Next, add the following lines, which define the “ORIGINATING” policy.
|
||||
|
||||
$policy\_bank{'ORIGINATING'} = { # mail supposedly originating from our users
|
||||
originating => 1, # declare that mail was submitted by our smtp client
|
||||
allow\_disclaimers => 1, # enables disclaimer insertion if available
|
||||
|
||||
# notify administrator of locally originating malware
|
||||
virus\_admin\_maps => \["virusalert\\@$mydomain"\],
|
||||
spam\_admin\_maps => \["virusalert\\@$mydomain"\],
|
||||
warnbadhsender => 1,
|
||||
|
||||
# force MTA conversion to 7-bit (e.g. before DKIM signing)
|
||||
smtpd\_discard\_ehlo\_keywords => \['8BITMIME'\],
|
||||
bypass\_banned\_checks\_maps => \[1\], # allow sending any file names and types
|
||||
terminate\_dsn\_on\_notify\_success => 0, # don't remove NOTIFY=SUCCESS option
|
||||
$undecipherable\_subject\_tag = '\*\*\*Encrypted Message\*\*\*',
|
||||
};
|
||||
|
||||
Save and close the file. Restart Amavis.
|
||||
|
||||
sudo systemctl restart amavis
|
||||
|
||||
Check its status to see if the restart is successful.
|
||||
|
||||
systemctl status amavis
|
||||
|
||||
Next, edit the Postfix master configuration file.
|
||||
|
||||
sudo nano /etc/postfix/master.cf
|
||||
|
||||
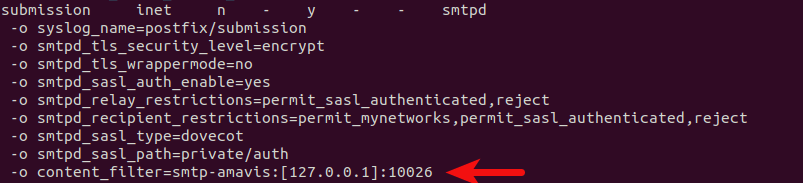
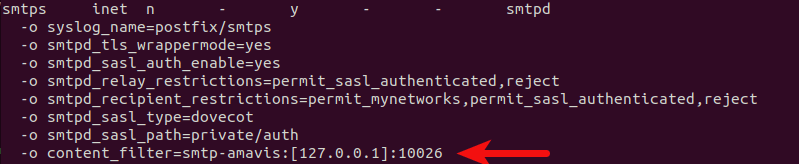
Add the following line to the `submission` service, so emails from authenticated SMTP clients will be passed to Amavis listening on port 10026. This line will override (`-o`) the `content_filter` parameter in `/etc/postfix/main.cf` file that we added in step 2.
|
||||
|
||||
-o content\_filter=smtp-amavis:\[127.0.0.1\]:10026
|
||||
|
||||
Like this:
|
||||
|
||||
|
||||
|
||||
If you have enabled the `smtps` service for Microsoft Outlook users, then you also need to add this line to the `smtps` service.
|
||||
|
||||
|
||||
|
||||
Save and close the file. Restart Postfix for the changes to take effect.
|
||||
|
||||
sudo systemctl restart postfix
|
||||
|
||||
Check its status to see if the restart is successful.
|
||||
|
||||
systemctl status postfix
|
||||
|
||||
## Step 5: Receive Virus Alert
|
||||
|
||||
You need to create an email address `virusalert@your-domain.com` to receive virus alerts from ClamAV. Note that you should create a real email address instead of creating an alias. ClamAV will bypass Postfix and submit alert emails directly to Dovecot, which isn’t configured to query aliases in the PostfixAdmin database.
|
||||
|
||||
## Spam Filtering in Amavis
|
||||
|
||||
**Note**: If you have followed my [SpamAssassin tutorial](https://www.linuxbabe.com/mail-server/block-email-spam-check-header-body-with-postfix-spamassassin), you don’t need to enable spam-checking in Amavis. If you enable it, each email will be checked twice by SpamAssassin.
|
||||
|
||||
To enable spam-checking in Amavis, install SpamAssassin and related packages.
|
||||
|
||||
sudo apt install spamassassin libnet-dns-perl libmail-spf-perl pyzor razor
|
||||
|
||||
Edit an Amavis configuration file.
|
||||
|
||||
sudo nano /etc/amavis/conf.d/15-content\_filter\_mode
|
||||
|
||||
Uncomment the following lines to enable spam-checking.
|
||||
|
||||
#@bypass\_spam\_checks\_maps = (
|
||||
# \\%bypass\_spam\_checks, \\@bypass\_spam\_checks\_acl, \\$bypass\_spam\_checks\_re);
|
||||
|
||||
Save and close the file. Then restart Amavis.
|
||||
|
||||
sudo systemctl restart amavis
|
||||
|
||||
## DKIM in Amavis
|
||||
|
||||
Two common pieces of software that can do DKIM signing and verification on Linux are OpenDKIM and Amavis. I prefer to use [OpenDKIM](https://www.linuxbabe.com/mail-server/setting-up-dkim-and-spf) because it works better with [OpenDMARC](https://www.linuxbabe.com/mail-server/opendmarc-postfix-ubuntu). So I won’t explain how to DKIM sign your email in Amavis.
|
||||
|
||||
By default, Amavis can verify the DKIM signature of incoming email messages. If you have OpenDKIM running on your mail server, then you can disable DKIM verification in Amavis.
|
||||
|
||||
sudo nano /etc/amavis/conf.d/21-ubuntu\_defaults
|
||||
|
||||
Find the following line and change `1` to `0`, so Amavis won’t verify DKIM signatures.
|
||||
|
||||
$enable\_dkim\_verification = 1;
|
||||
|
||||
Save and close the file. Then restart Amavis.
|
||||
|
||||
sudo systemctl restart amavis
|
||||
|
||||
When receiving incoming emails, Postfix will call OpenDKIM via the sendmail milter interface to verify DKIM signatures, then pass the email to Amavis for virus-checking. When sending outgoing emails, Postfix will call OpenDKIM to sign the emails, then pass them to Amavis for virus-checking.
|
||||
|
||||
## Improving Amavis Performance
|
||||
|
||||
By default, Amavis runs 2 processes. If you see the following lines in the mail log (`/var/log/mail.log`), it means Amavis can’t process emails fast enough.
|
||||
|
||||
postfix/qmgr\[1619188\]: warning: mail for \[127.0.0.1\]:10024 is using up 4001 of 4008 active queue entries
|
||||
postfix/qmgr\[1619188\]: warning: you may need to reduce smtp-amavis connect and helo timeouts
|
||||
postfix/qmgr\[1619188\]: warning: so that Postfix quickly skips unavailable hosts
|
||||
postfix/qmgr\[1619188\]: warning: you may need to increase the main.cf minimal\_backoff\_time and maximal\_backoff\_time
|
||||
postfix/qmgr\[1619188\]: warning: so that Postfix wastes less time on undeliverable mail
|
||||
mail postfix/qmgr\[1619188\]: warning: you may need to increase the master.cf smtp-amavis process limit
|
||||
mail postfix/qmgr\[1619188\]: warning: please avoid flushing the whole queue when you have
|
||||
mail postfix/qmgr\[1619188\]: warning: lots of deferred mail, that is bad for performance
|
||||
|
||||
To improve performance, edit Amavis configuration file.
|
||||
|
||||
sudo nano /etc/amavis/conf.d/50-user
|
||||
|
||||
Add the following line in the file between the `use strict;` and `1;` line. This will make Amavis run 4 processes. If you have 10 CPU cores, you can change 4 to 10. Note that running more than 10 Amavis processes has little effect on performance.
|
||||
|
||||
$max\_servers = 4;
|
||||
|
||||
Save and close the file. Then edit the Postifx master configuration file.
|
||||
|
||||
sudo nano /etc/postfix/master.cf
|
||||
|
||||
Find the `smtp-amavis` service definition, and change the process limit from 2 to 4.
|
||||
|
||||
smtp-amavis unix - - n - **4** smtp
|
||||
-o syslog\_name=postfix/amavis
|
||||
-o smtp\_data\_done\_timeout=1200
|
||||
-o smtp\_send\_xforward\_command=yes
|
||||
-o disable\_dns\_lookups=yes
|
||||
-o max\_use=20
|
||||
-o smtp\_tls\_security\_level=none
|
||||
|
||||
Save and close the file. Then restart Amavis and Postfix for the changes to take effect.
|
||||
|
||||
sudo systemctl restart amavis postfix
|
||||
|
||||
Now run the following command. You should see that there are 4 Amavis processes now.
|
||||
|
||||
sudo amavisd-nanny
|
||||
|
||||

|
||||
|
||||
Press `Ctrl+C` to stop amavisd-nanny.
|
||||
|
||||
## Skip Virus-Checking for Your Newsletters
|
||||
|
||||
If you [use your mail server to send newsletters](https://www.linuxbabe.com/ubuntu/install-mautic-self-hosted-email-marketing-ubuntu-20-04), and you enable Amavis and ClamAV, then lots of CPU and RAM resources will be used for virus-checking when you send newsletters to your subscribers. It could make your mail server unresponsive. You can skip virus-checking for your newsletters by using the method below.
|
||||
|
||||
Edit the Postfix master configuration file.
|
||||
|
||||
sudo nano /etc/postfix/master.cf
|
||||
|
||||
Add the following lines at the beginning of this file. This will enable `smtpd` on port 2525 of the localhost and it can accept client connections initiated from the same server. If there’s another process listening on port 2525, you can change 127.0.0.1:2525 to something else, like 127.0.0.1:2552. Note that the `content_filter` parameter is set to `none`, which means emails won’t be scanned by ClamAV.
|
||||
|
||||
127.0.0.1:2525 inet n - - - 1 smtpd
|
||||
-o syslog\_name=postfix/2525
|
||||
-o postscreen\_greet\_action=ignore
|
||||
-o content\_filter=
|
||||
|
||||
Then add the following lines at the end of this file. Replace 12.34.56.78 with the mail server’s public IP address. This will create another Postfix submission daemon listening on port 10587. This is for client connections from another server.
|
||||
|
||||
12.34.56.78:10587 inet n - y - - smtpd
|
||||
-o syslog\_name=postfix/10587
|
||||
-o smtpd\_tls\_security\_level=encrypt
|
||||
-o smtpd\_tls\_wrappermode=no
|
||||
-o smtpd\_sasl\_auth\_enable=yes
|
||||
-o smtpd\_relay\_restrictions=permit\_sasl\_authenticated,reject
|
||||
-o smtpd\_recipient\_restrictions=permit\_mynetworks,permit\_sasl\_authenticated,reject
|
||||
-o smtpd\_sasl\_type=dovecot
|
||||
-o smtpd\_sasl\_path=private/auth
|
||||
-o content\_filter=
|
||||
|
||||
Save and close the file. Then Restart postfix.
|
||||
|
||||
sudo systemctl restart postfix
|
||||
|
||||
If your newsletter application runs on the mail server, then specify `127.0.0.1:2525` as the SMTP host, without SMTP authentication. If your newsletter application runs on a different server, then specify `12.34.56.78:10587` as the SMTP host, with SMTP authentication.
|
||||
|
||||
## Troubleshooting
|
||||
|
||||
If your Postfix SMTP server can’t send outgoing emails, and you find the following error message in the mail log (`/var/log/mail.log`),
|
||||
|
||||
relay=none, delay=239, delays=239/0.04/0/0, dsn=4.3.0, status=deferred (server unavailable or unable to receive mail)
|
||||
|
||||
it could be that amavis is not running, so you need to check its status:
|
||||
|
||||
sudo systemctl status amavis
|
||||
|
||||
You can restart it with:
|
||||
|
||||
sudo systemctl restart amavis
|
||||
|
||||
Another cause for this error is that you are enforcing TLS connection for Postfix when sending outgoing emails with the following setting in the `/etc/postfix/main.cf` file.
|
||||
|
||||
smtp\_tls\_security\_level = enforce
|
||||
|
||||
Since Postfix can’t establish TLS connection to Amavis, so the email is deferred. You should use the following setting.
|
||||
|
||||
smtp\_tls\_security\_level = may
|
||||
|
||||
Then restart Postfix.
|
||||
|
||||
## Using ClamAV to Scan Virus for the Linux File System
|
||||
|
||||
While the main topic of this article is virus scanning for emails, since ClamAV is installed on the server, why not use it to scan viruses for other files?
|
||||
|
||||
First, edit the ClamAV configuration file.
|
||||
|
||||
sudo nano /etc/clamav/clamd.conf
|
||||
|
||||
Find the following line:
|
||||
|
||||
MaxDirectoryRecursion 15
|
||||
|
||||
The default maximum depth directories scanned by ClamAV is 15, you probably want to change it to a bigger number to avoid the “directory recursion limit reached” warning.
|
||||
|
||||
MaxDirectoryRecursion 30
|
||||
|
||||
Then find the following two lines.
|
||||
|
||||
MaxScanSize 100M
|
||||
MaxFileSize 25M
|
||||
|
||||
The default max scan size is 100M and the max file size is 25M. It’s likely that your server has files of more than 100M. The default config will produce the following errors when the file size exceeds the limit.
|
||||
|
||||
LibClamAV Warning: PNG: Unexpected early end-of-file.
|
||||
LibClamAV Warning: cli\_scanxz: decompress file size exceeds limits - only scanning 27262976 bytes
|
||||
|
||||
You can increase the scan size like:
|
||||
|
||||
MaxScanSize 2048M
|
||||
MaxFileSize 2048M
|
||||
|
||||
Linux has many special files in `/proc/`, `/sys/`, `/run/`, `/dev/`, `/snap/` and `/var/lib/lxcfs/cgroup/` directory that should not be scanned, so you need to exclude them in ClamAV by adding the following lines at the end of this file.
|
||||
|
||||
ExcludePath ^/proc
|
||||
ExcludePath ^/sys
|
||||
ExcludePath ^/run
|
||||
ExcludePath ^/dev
|
||||
ExcludePath ^/snap
|
||||
ExcludePath ^/var/lib/lxcfs/cgroup
|
||||
|
||||
Save and close the file. Then restart `clamav-daemon.service` for the changes to take effect.
|
||||
|
||||
sudo systemctl restart clamav-daemon
|
||||
|
||||
Wait a few seconds for `clamav-daemon.service` to finish restarting. Next, you can start scanning with:
|
||||
|
||||
sudo clamdscan --fdpass /
|
||||
|
||||
This will scan the entire Linux file system, excluding the directories we mentioned earlier. To make ClamAV scan the file sytem automatically, edit the root user’s crontab file.
|
||||
|
||||
sudo crontab -e
|
||||
|
||||
Add the following line to this file. ClamAV will scan the entire file system at 5:10AM every day.
|
||||
|
||||
10 5 \* \* \* /usr/bin/clamdscan --fdpass /
|
||||
|
||||
Save and close the file.
|
||||
|
||||
**Hint #1**: There’s another utility called `clamscan` that can also be used for virus scanning. However, `clamscan` doesn’t use the virus definition database that’s already loaded in memory. It will load a separate copy of virus definition database into memory again, wasting server resources.`clamscan` is also slower than `clamdscan`, so I don’t recommend it.
|
||||
|
||||
**Hint #2**: If there are a huge number of files on your server, `clamdscan` will use lots of CPU resources.
|
||||
|
||||
## Wrapping Up
|
||||
|
||||
I hope this tutorial helped you set up Amavis and ClamAV on Ubuntu mail server. As always, if you found this post useful, then [subscribe to our free newsletter](https://newsletter.linuxbabe.com/subscription/wkeY5d6pg) to get more tips and tricks. Take care 🙂
|
||||
Reference in New Issue
Block a user